Showing 120 of 120on this page. Filters & sort apply to loaded results; URL updates for sharing.120 of 120 on this page
Logs do AD on-premises no Microsoft Sentinel - Daniel Donda
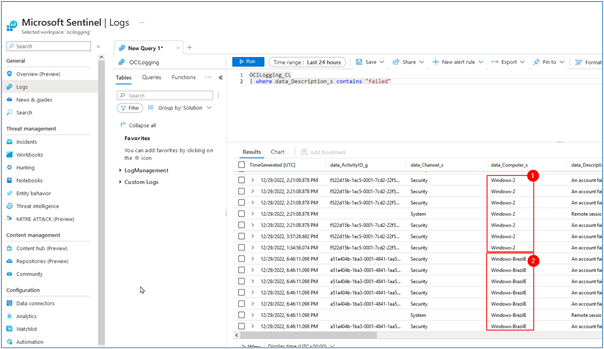
Ingest Oracle Cloud Infrastructure logs into Microsoft Azure Sentinel ...
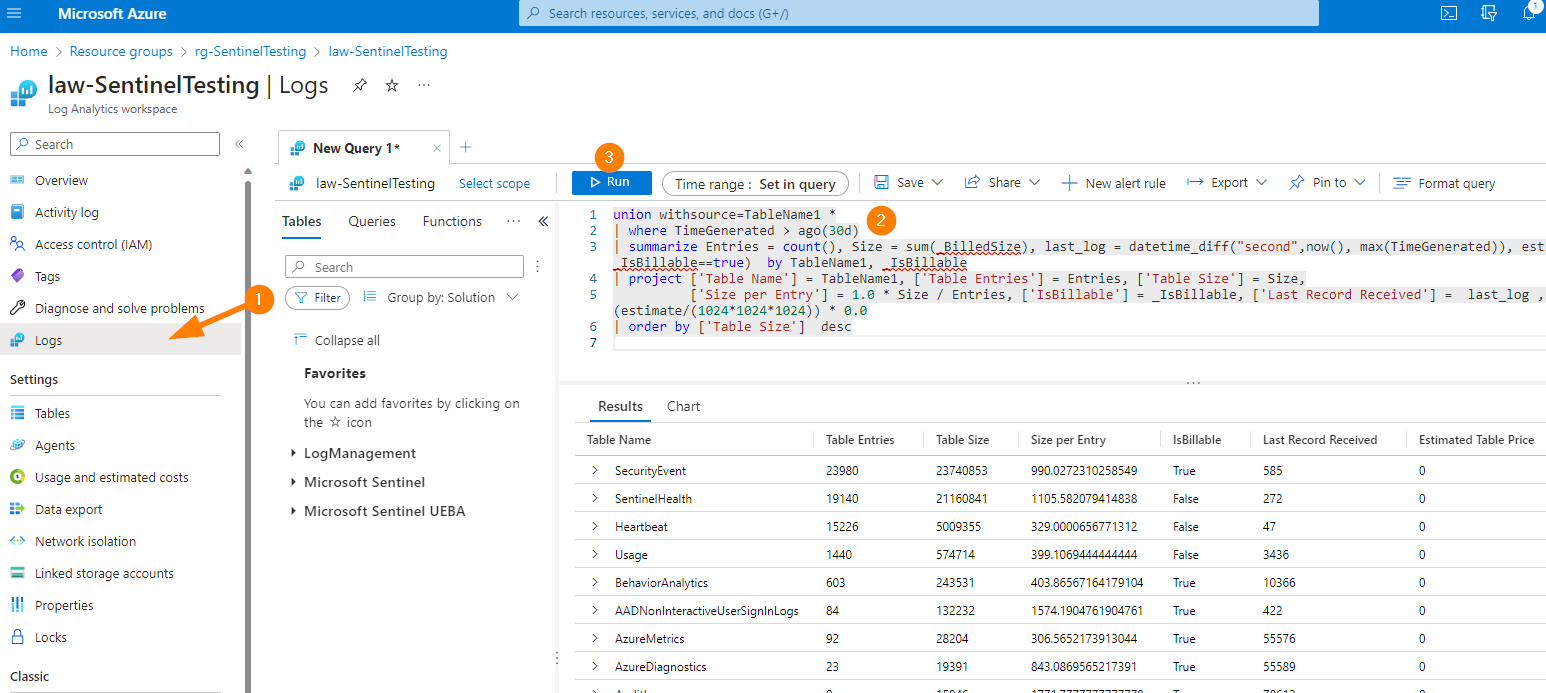
sk154872 - Microsoft Sentinel / Azure Log Analytics: Example ...
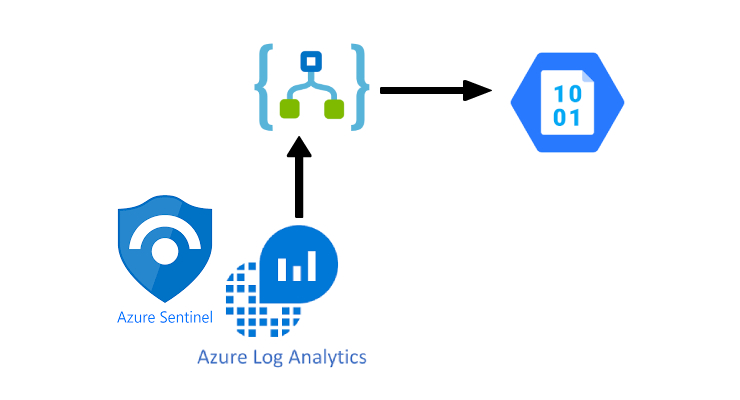
Move Microsoft Sentinel Logs to Long-Term Storage
Forward Logs to Microsoft Sentinel with a Private Link 43
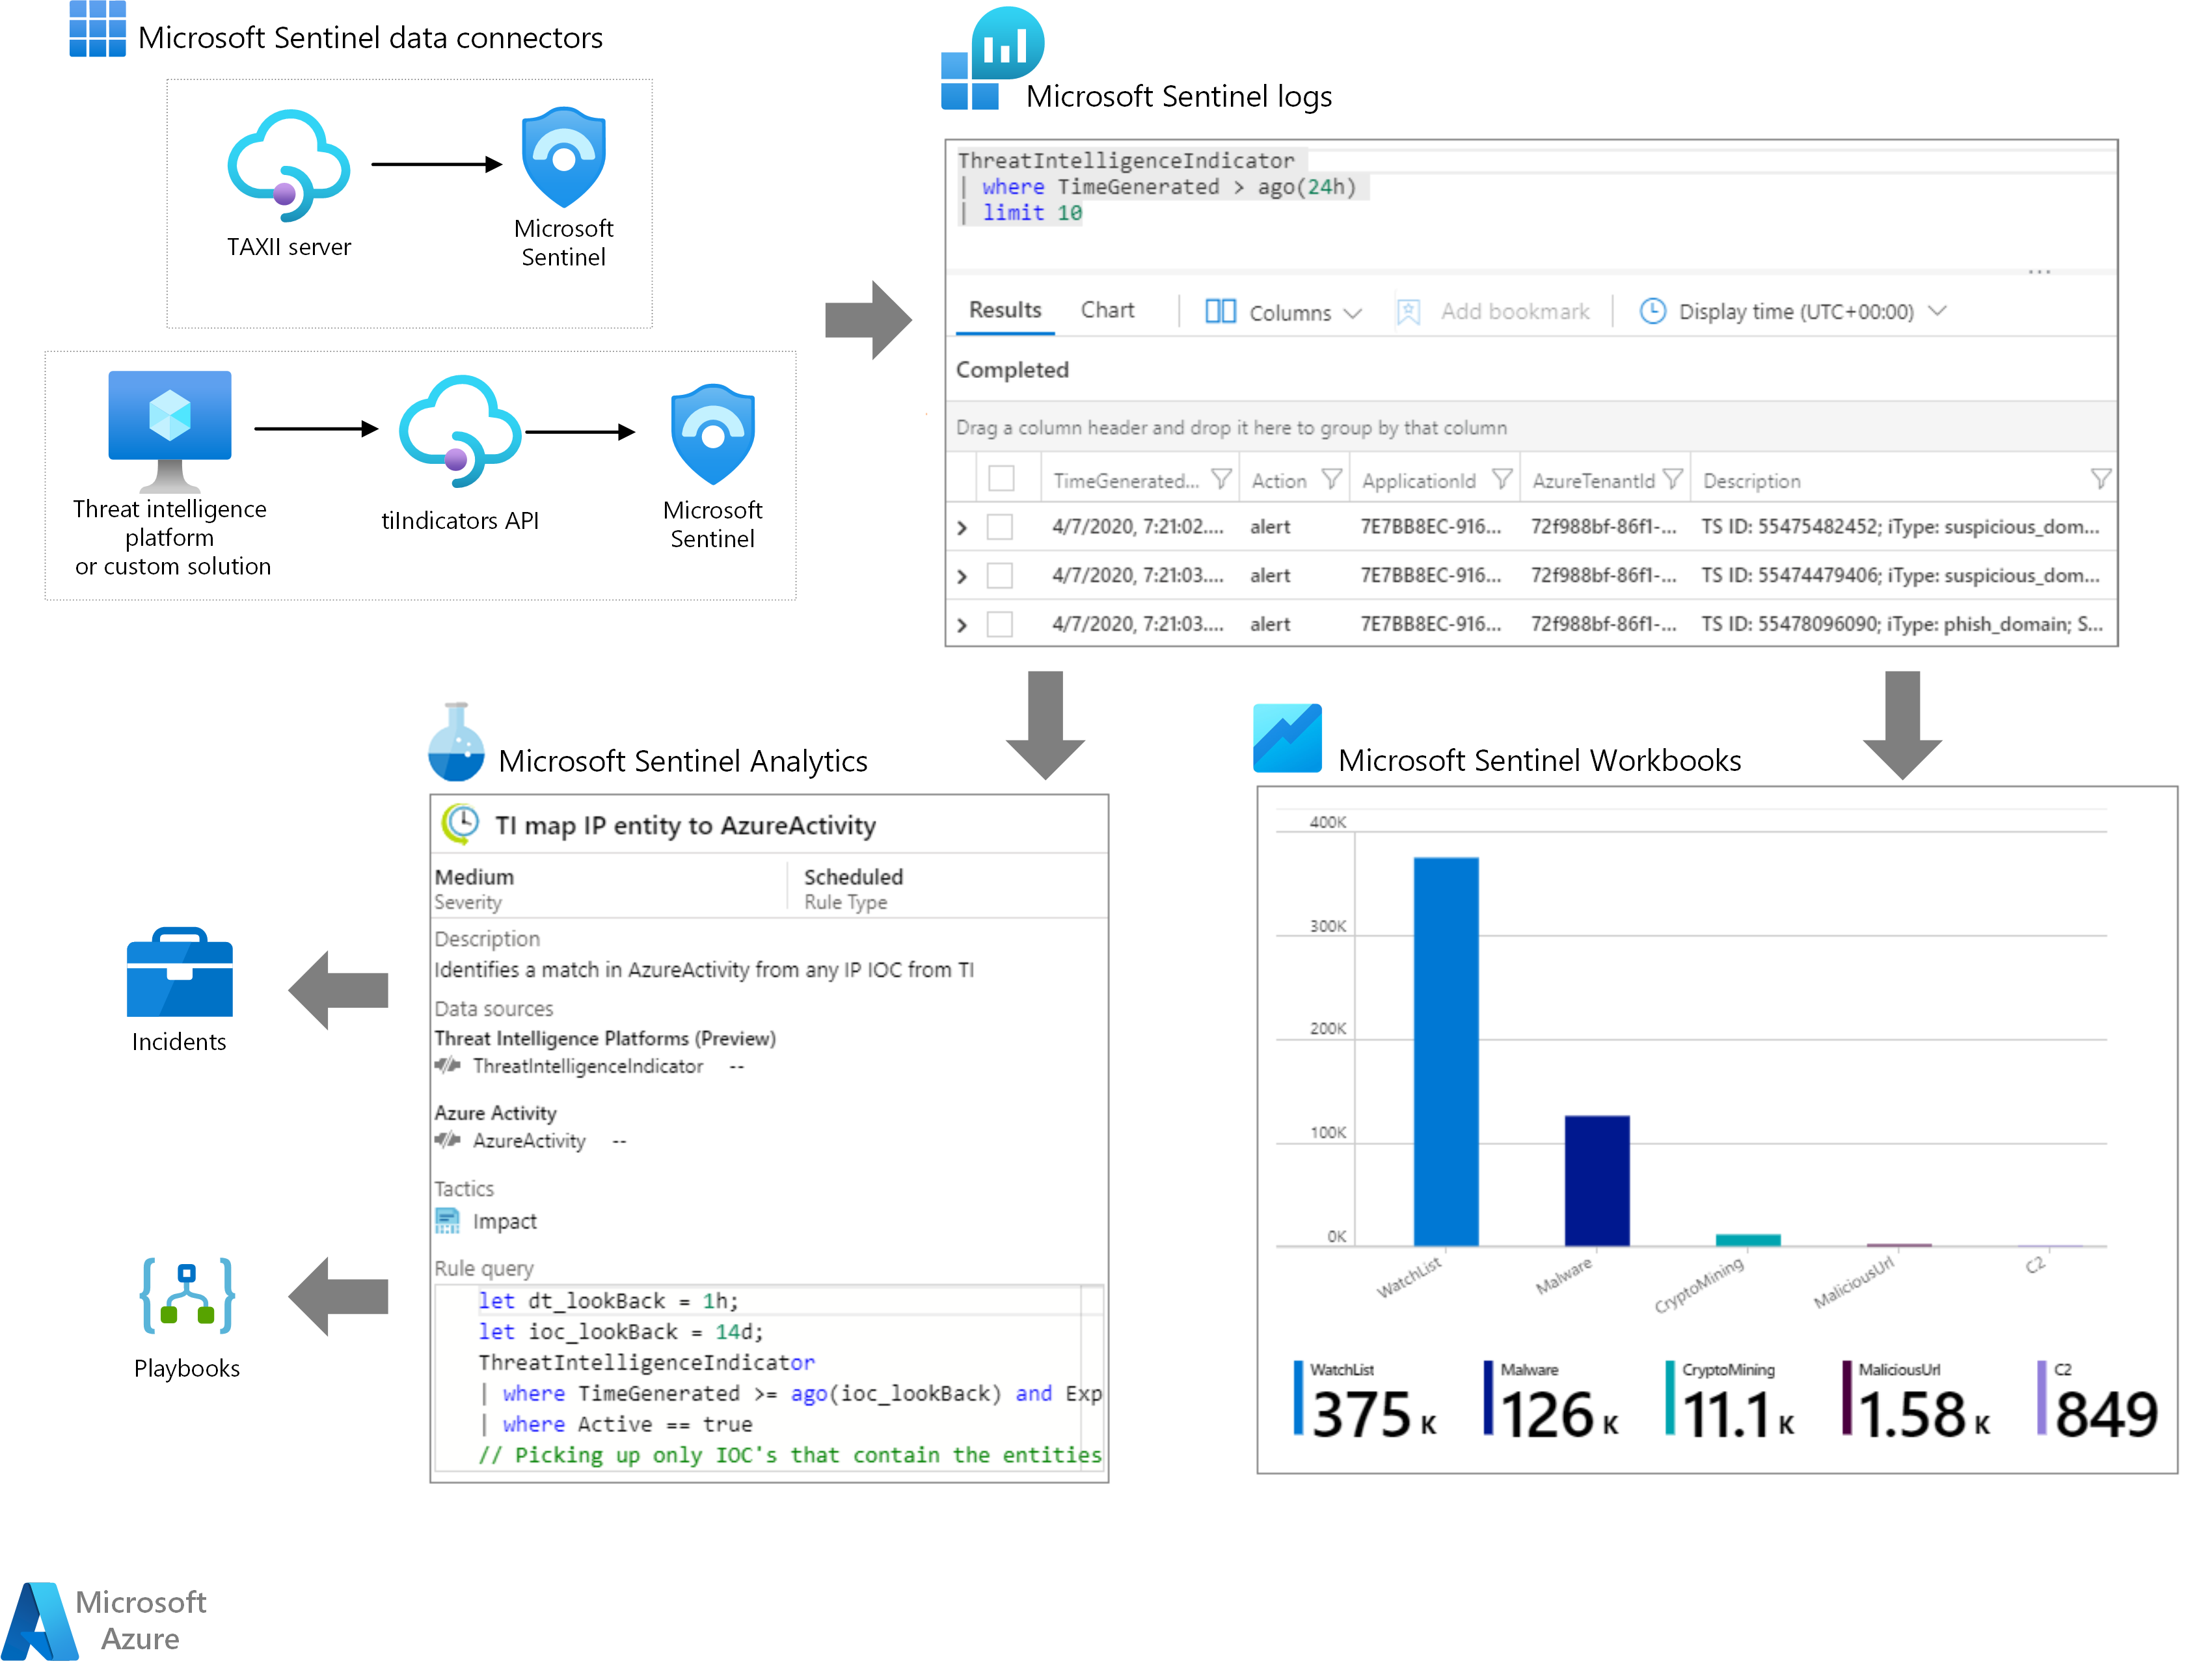
Cyber threat intelligence in Microsoft Sentinel - Azure Example ...
Optimize Sentinel Logs for Intune via Defender XDR - Patch My PC
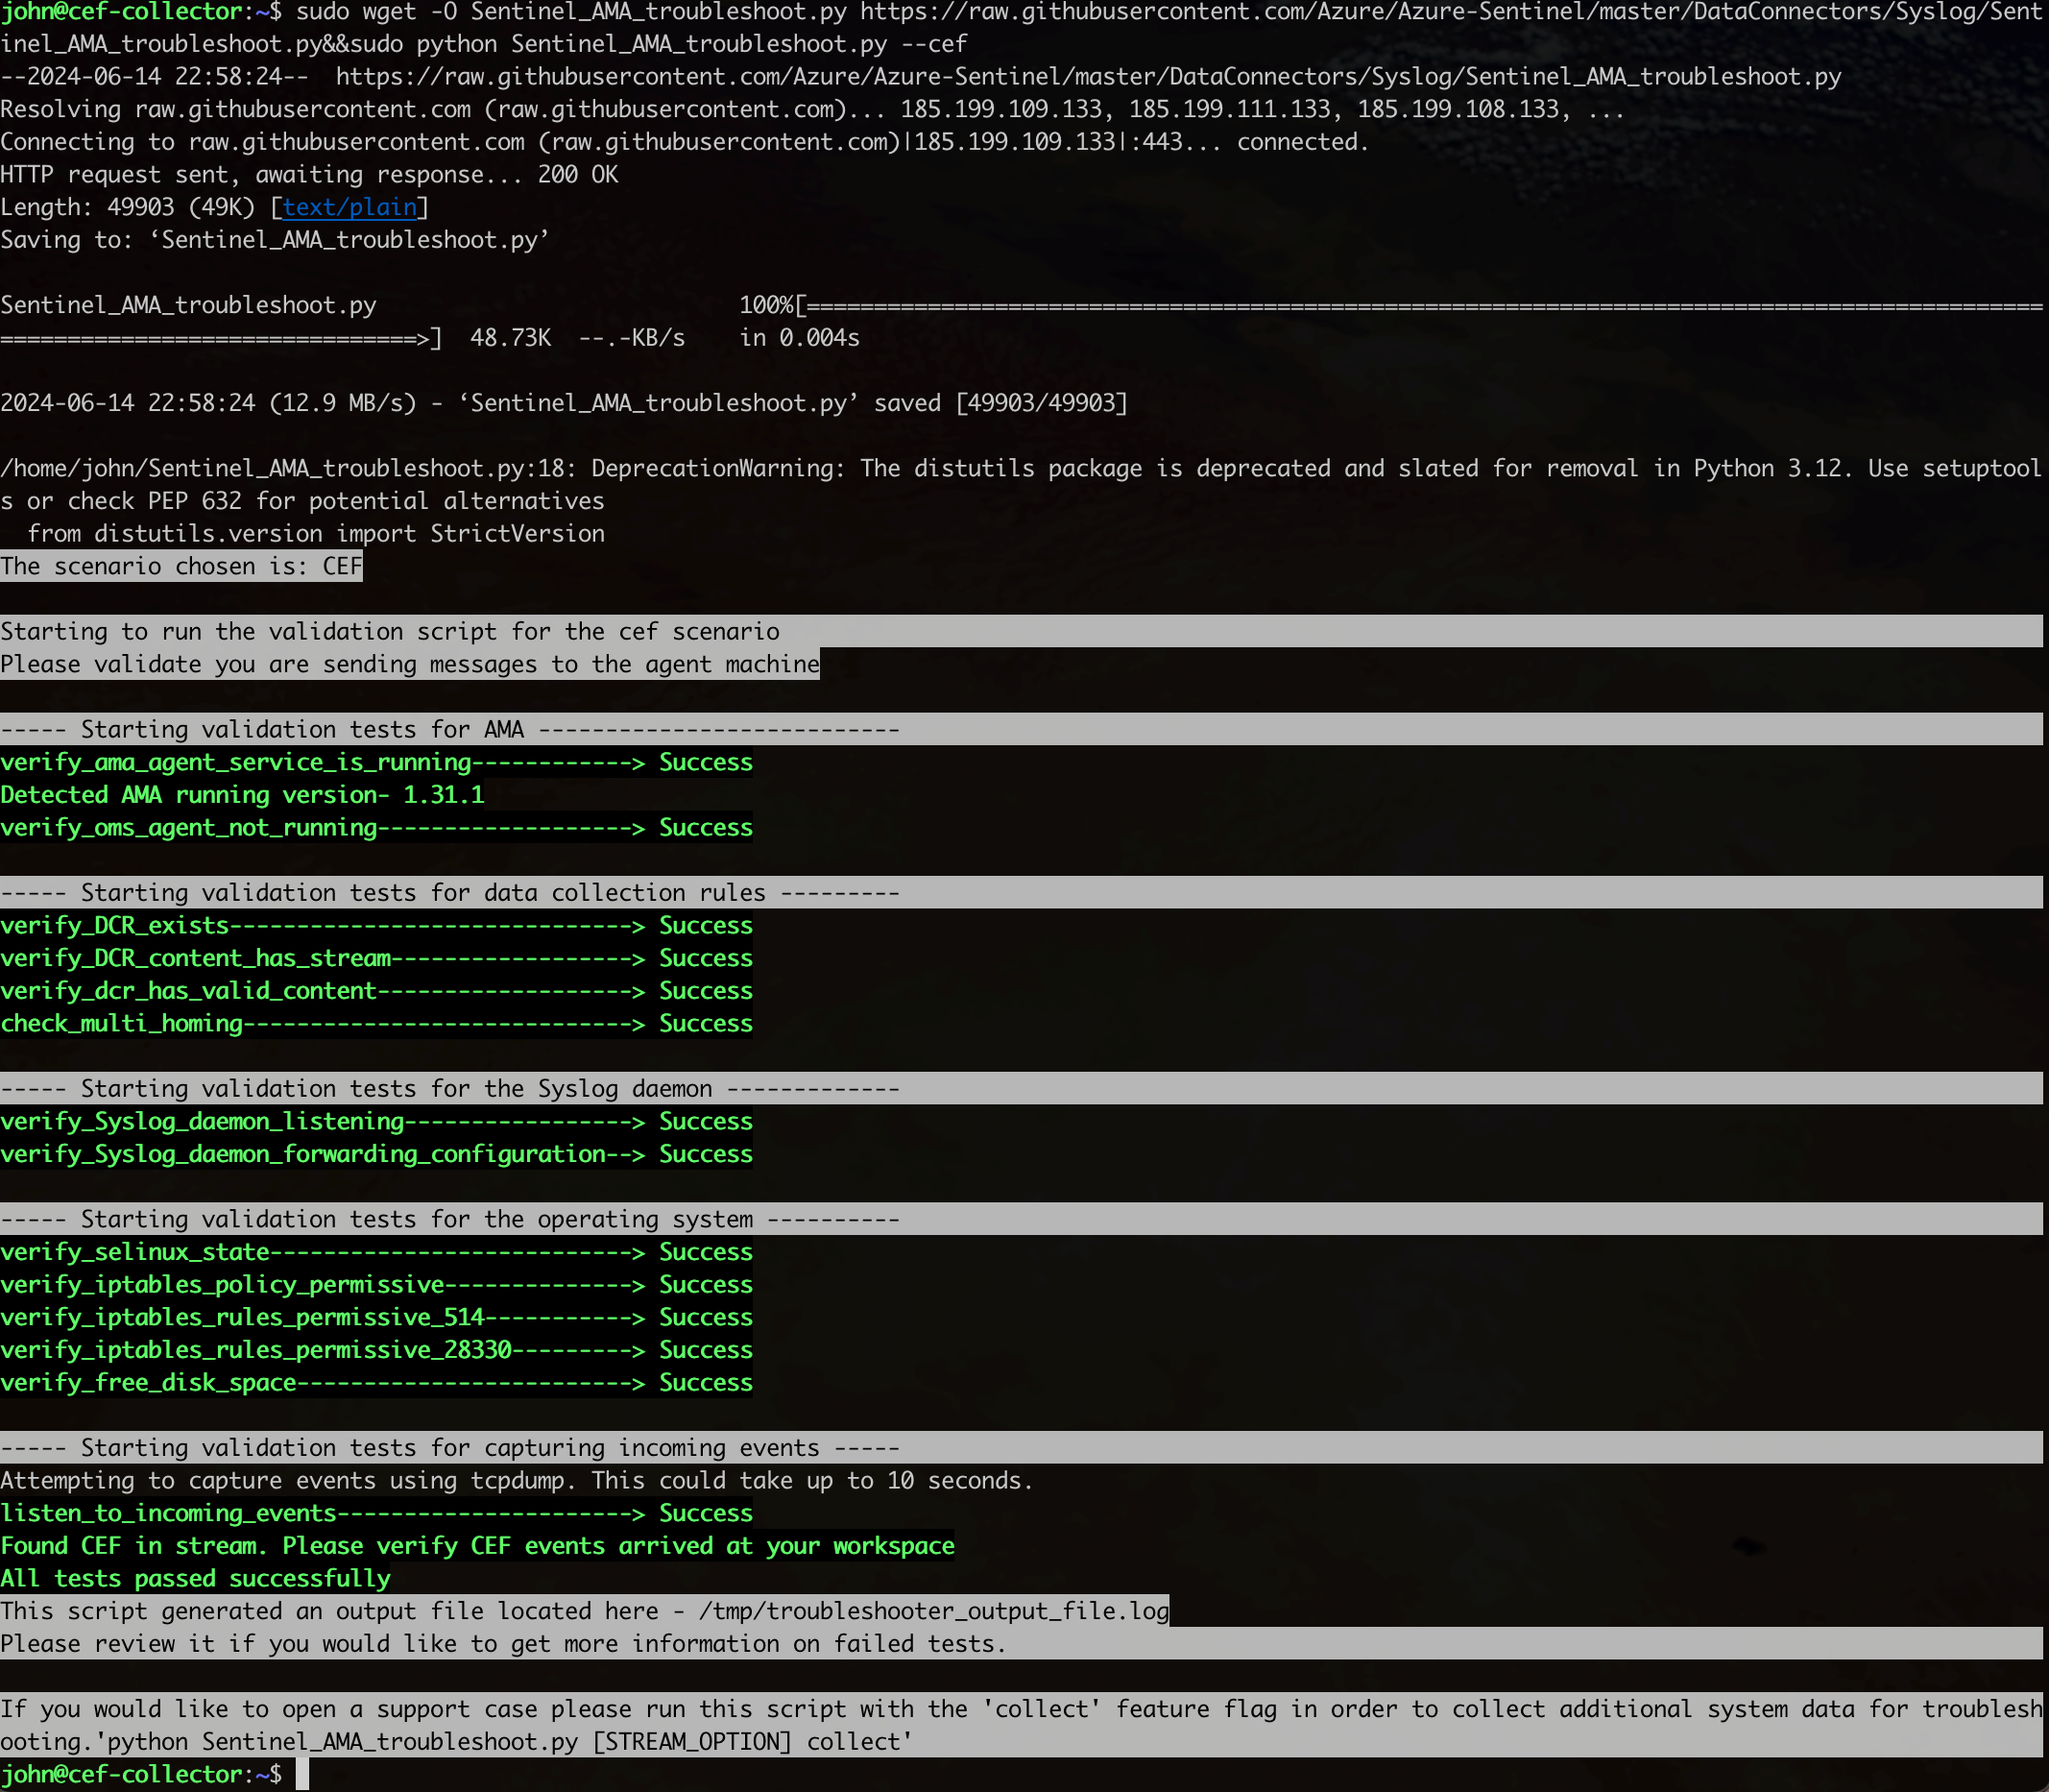
Simulate And Validate CEF Logs To Microsoft Sentinel - CHARBEL NEMNOM ...
Sending Cribl internal logs to Microsoft Sentinel using a custom table ...
Sentinel Log Format – Microsoft Sentinel Logs – SQMKS
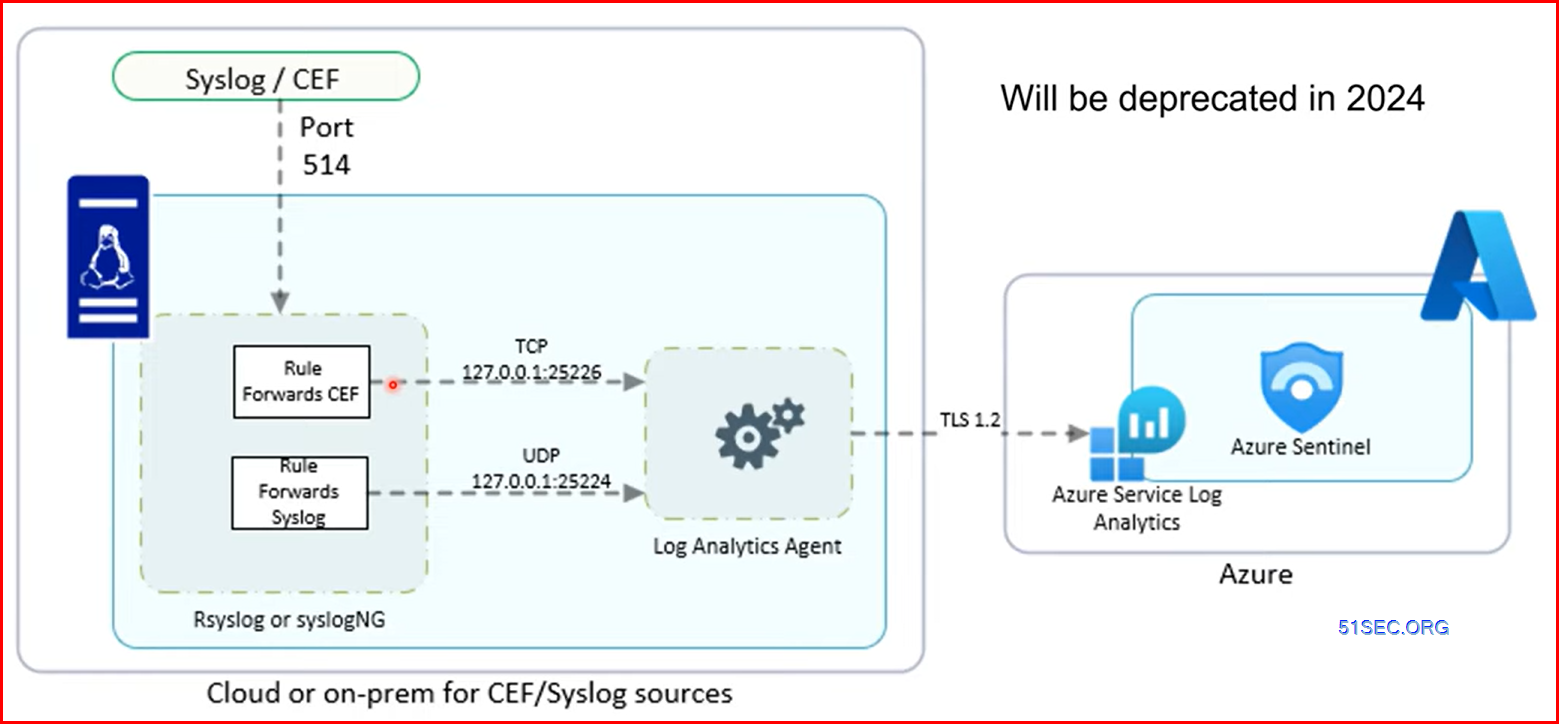
Effective Approach To Collect Linux Logs to Microsoft Sentinel 26
Ingest and analyze AWS security logs in Microsoft Sentinel - AWS ...
How to optimize logs in Microsoft Sentinel | ☁️ Charbel N. posted on ...
Microsoft Sentinel & Azure Arc - Troubleshooting Windows Event Logs ...
Effective Approach To Collect Linux Logs to Microsoft Sentinel 12
Microsoft Sentinel - Ingesting Intune Logs - Gennaro Migliaccio
Sending logs to Microsoft Sentinel with NXLog | NXLog Blog
Custom Logs in Sentinel not triggering incidents or showing up in ...
Azure Sentinel – logs retention | A Security Engineer
Microsoft Sentinel - Archiving Logs Guide - Gennaro Migliaccio
Microsoft Sentinel Event Logs _ When to use Basic Logs – PESY
Forward Logs to Microsoft Sentinel with a Private Link 44
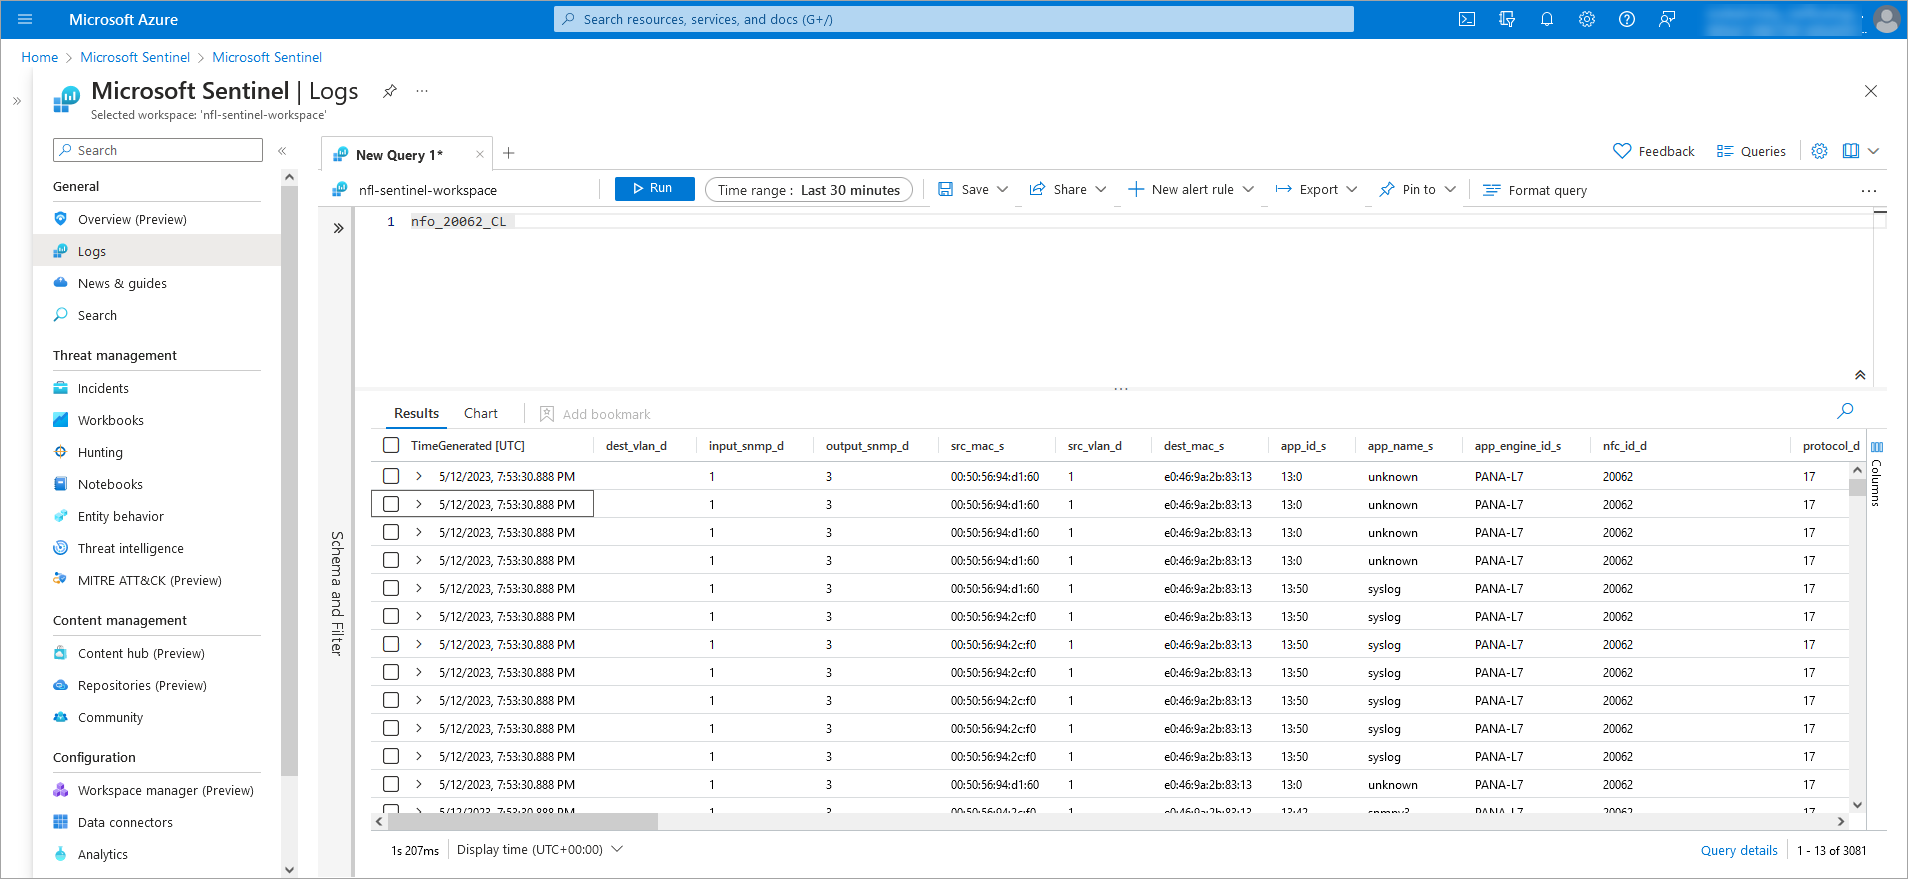
Microsoft Sentinel Integration | NetFlow Logic
Translate raw security logs to behavioral insights using UEBA behaviors ...
What Is Microsoft (Azure) Sentinel and Why Do We Need It?
Sentinel lab - Hybrid + Identity Cyber Range
Optimize Log Ingestion And Access In Microsoft Sentinel - CHARBEL ...
Microsoft Sentinel Activity Log – FXOECZ
Sentinel Log Forwarder
Optimize Microsoft Sentinel Log Retention With Azure Data Explorer ...
Onboard to Microsoft Sentinel | Microsoft Learn
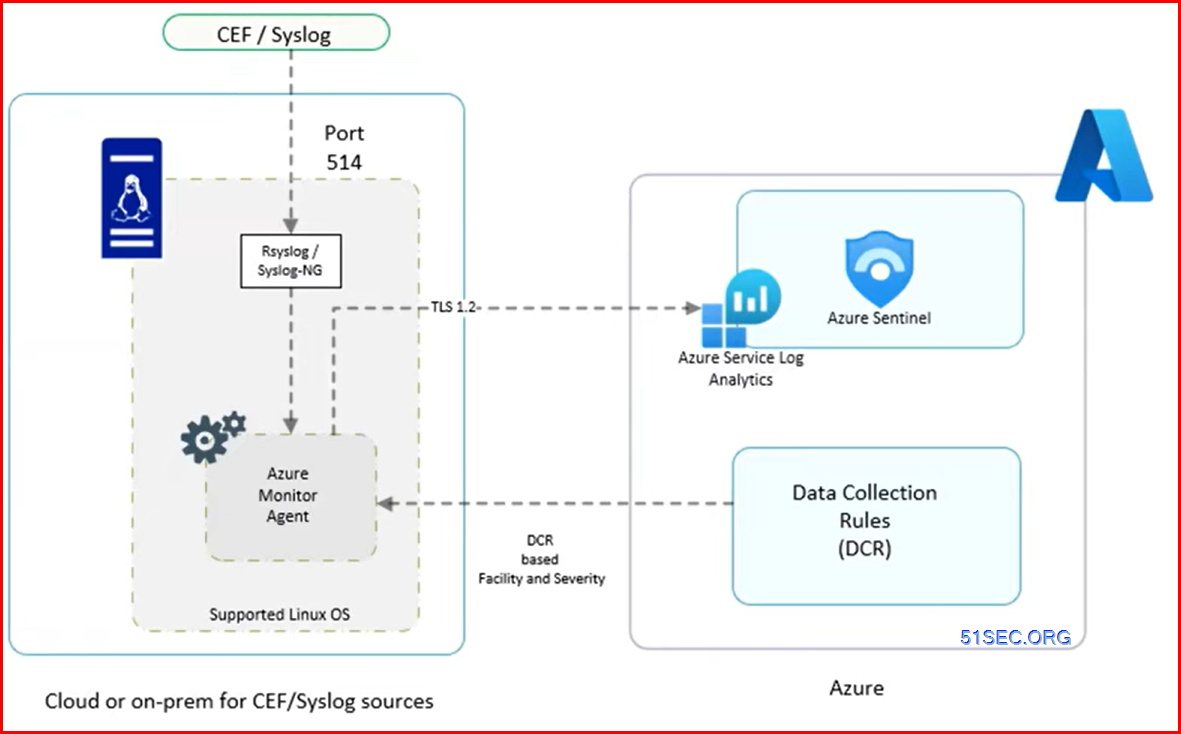
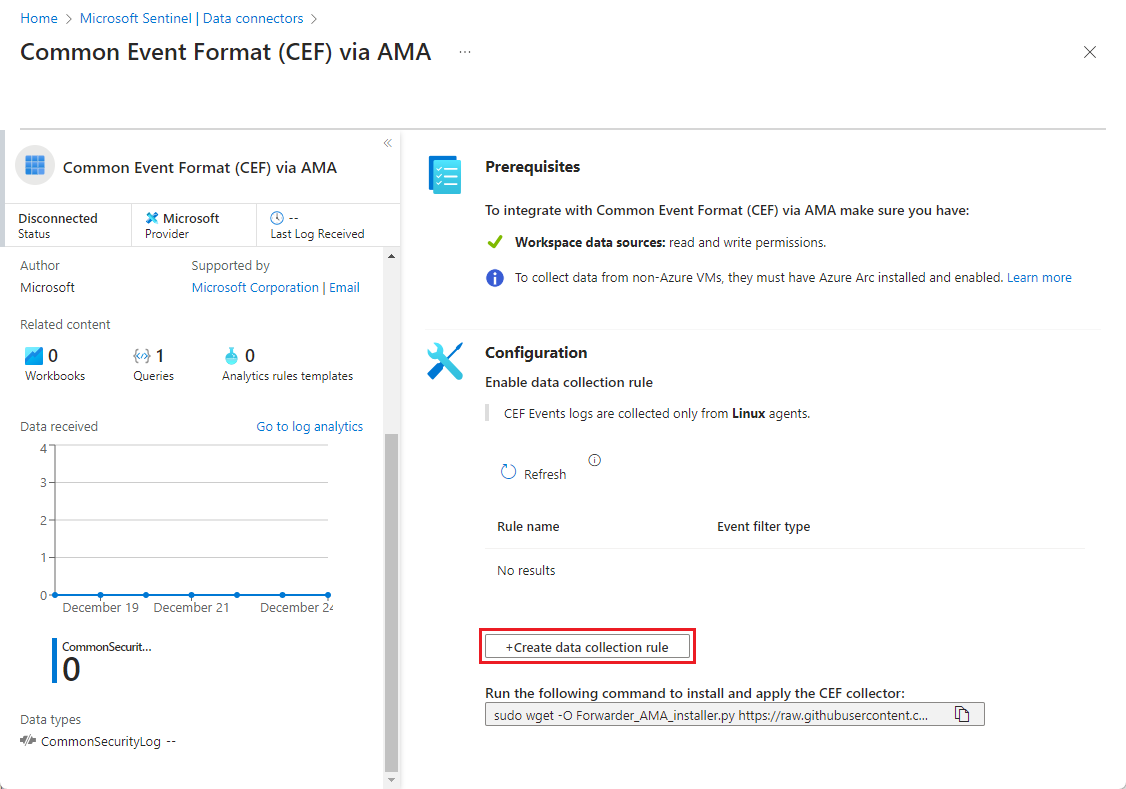
Configuring Sentinel to Collect CEF Syslog with the AMA agent – Simple ...
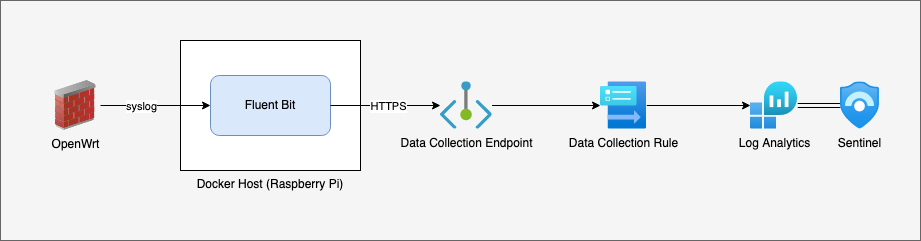
Set Up HTTPS Log Forwarding to Microsoft Sentinel
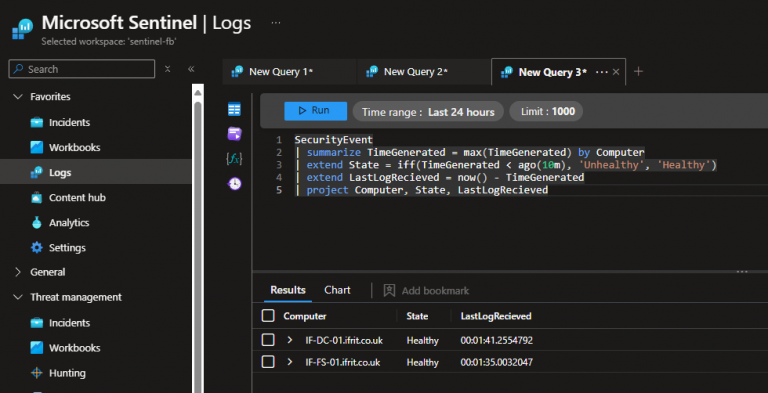
Monitor the health of the connection between Microsoft Sentinel and ...
Sentinelone Access Logs | How To Collect Logs – MKDOKR
Logging User Access Admin elevations to Microsoft Sentinel | Adriaans ...
Microsoft Sentinel integration – Help Center
Azure Sentinel Log Query Scripts Collection : KQL (Kusto Query Language ...
Auxiliary Logs Transformations in Microsoft Sentinel: A Step-by-Step ...
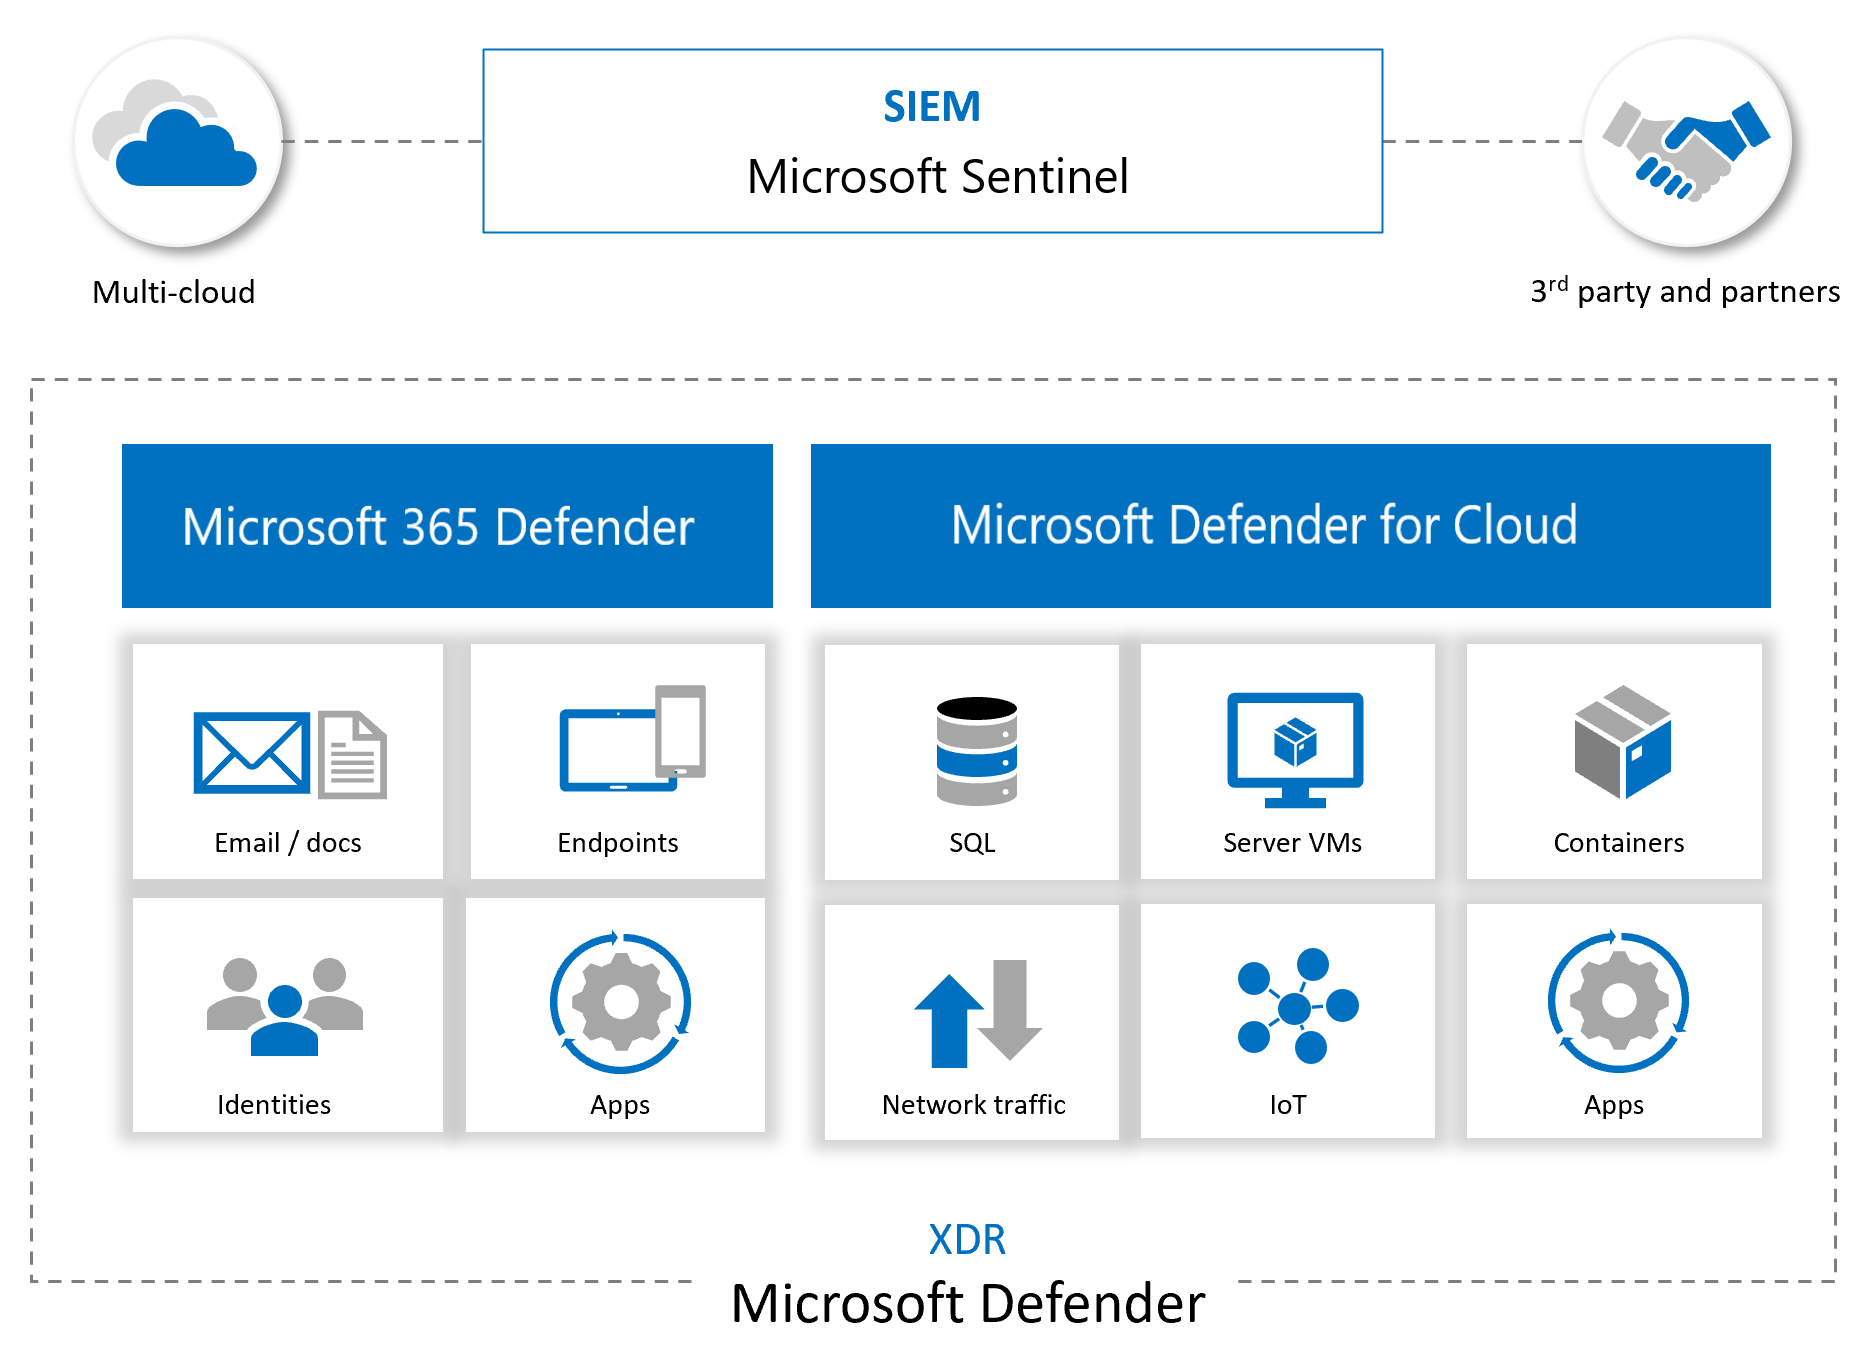
Microsoft Sentinel
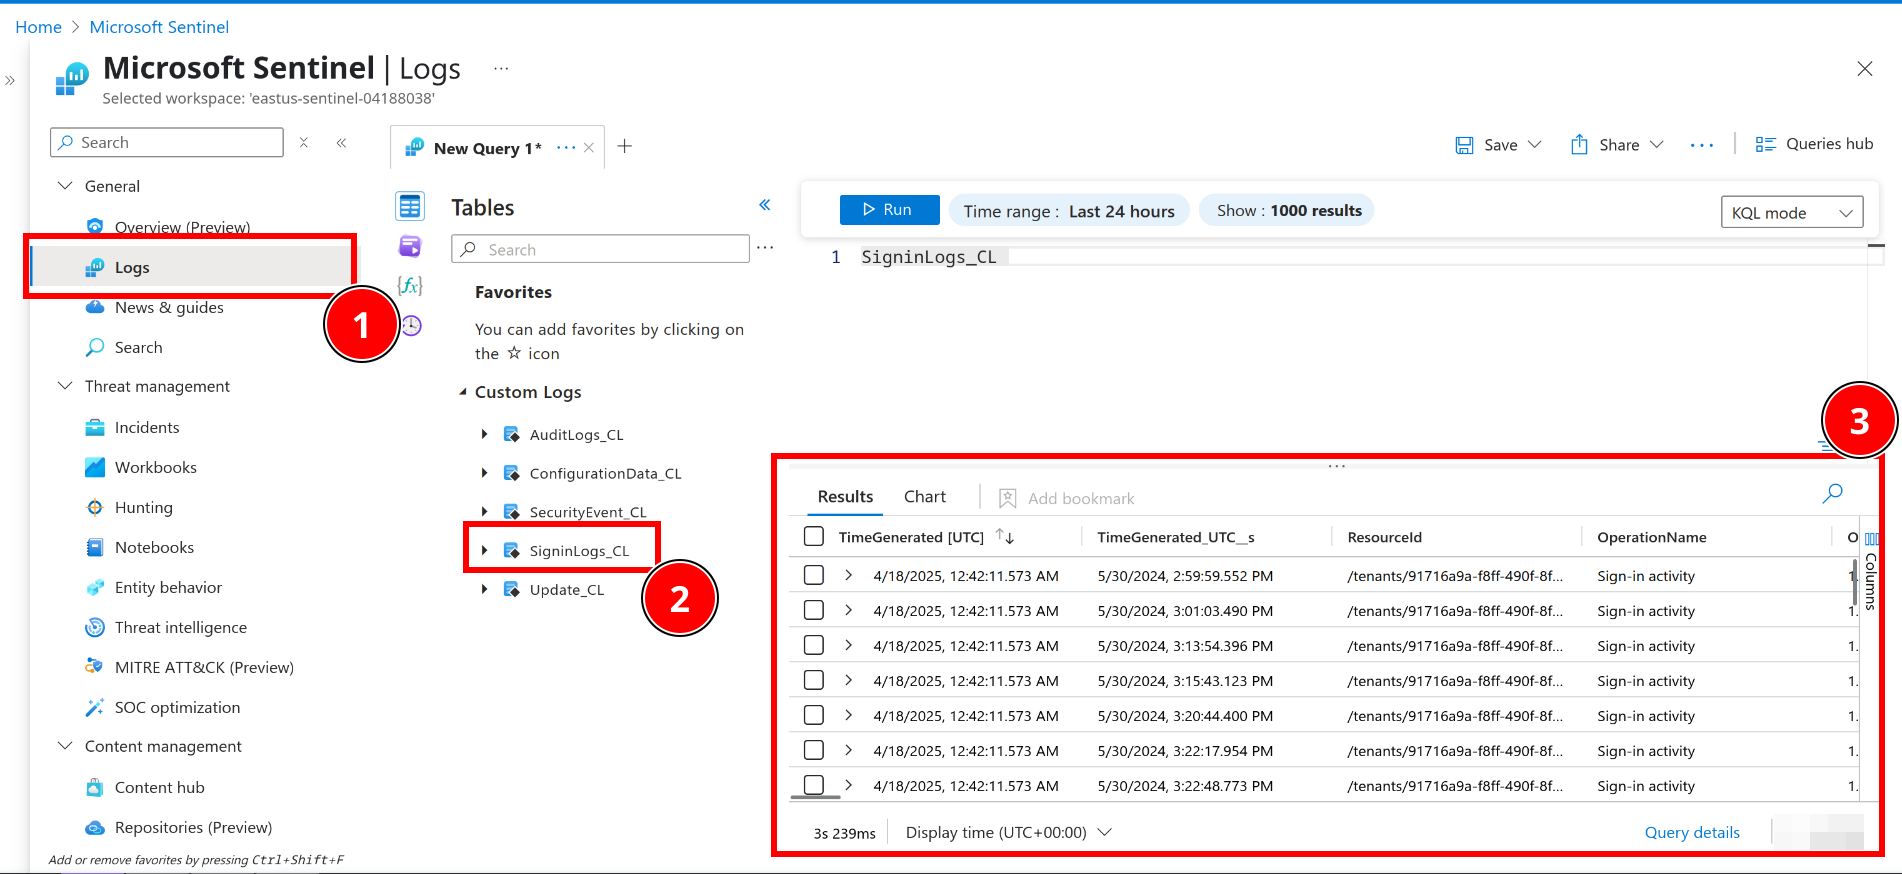
Ingest Custom Logs to Microsoft Sentinel: A Step-by-Step Guide 1
Logstash Azure Log Analytics | Logstash: Collect, Parse, Transform Logs ...
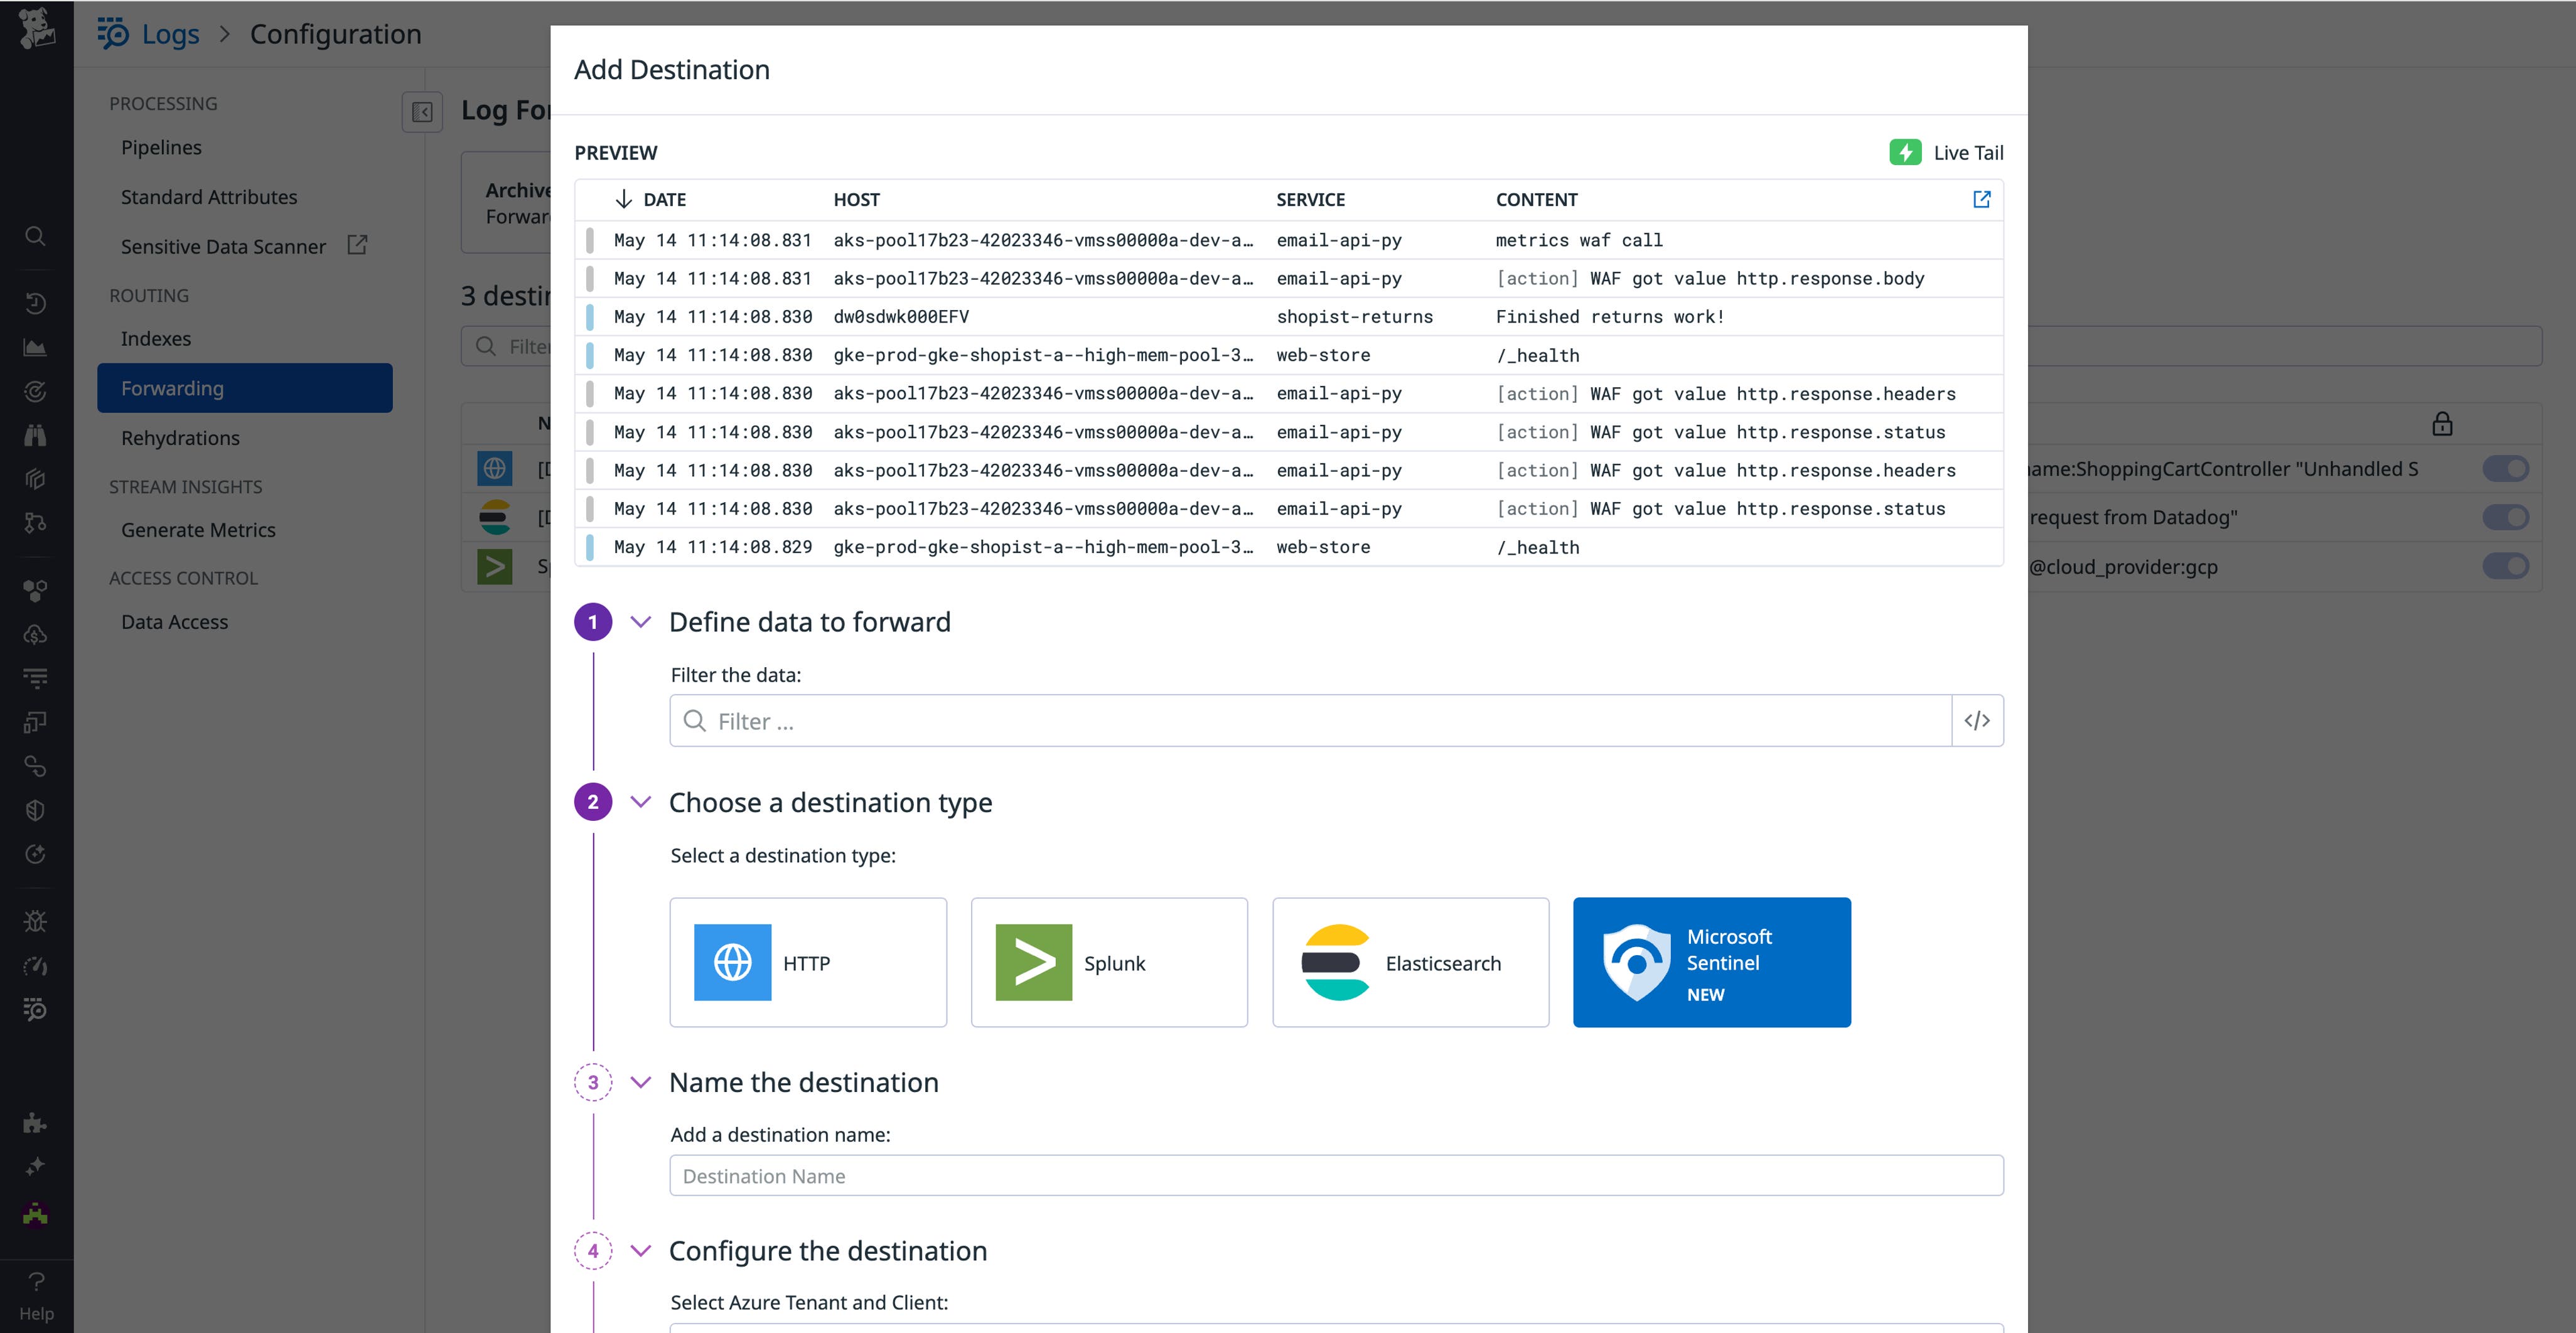
Simplify your SIEM migration to Microsoft Sentinel with Datadog ...
Sentinel & Log Analytics – How to Create Incidents to Test with – Part ...
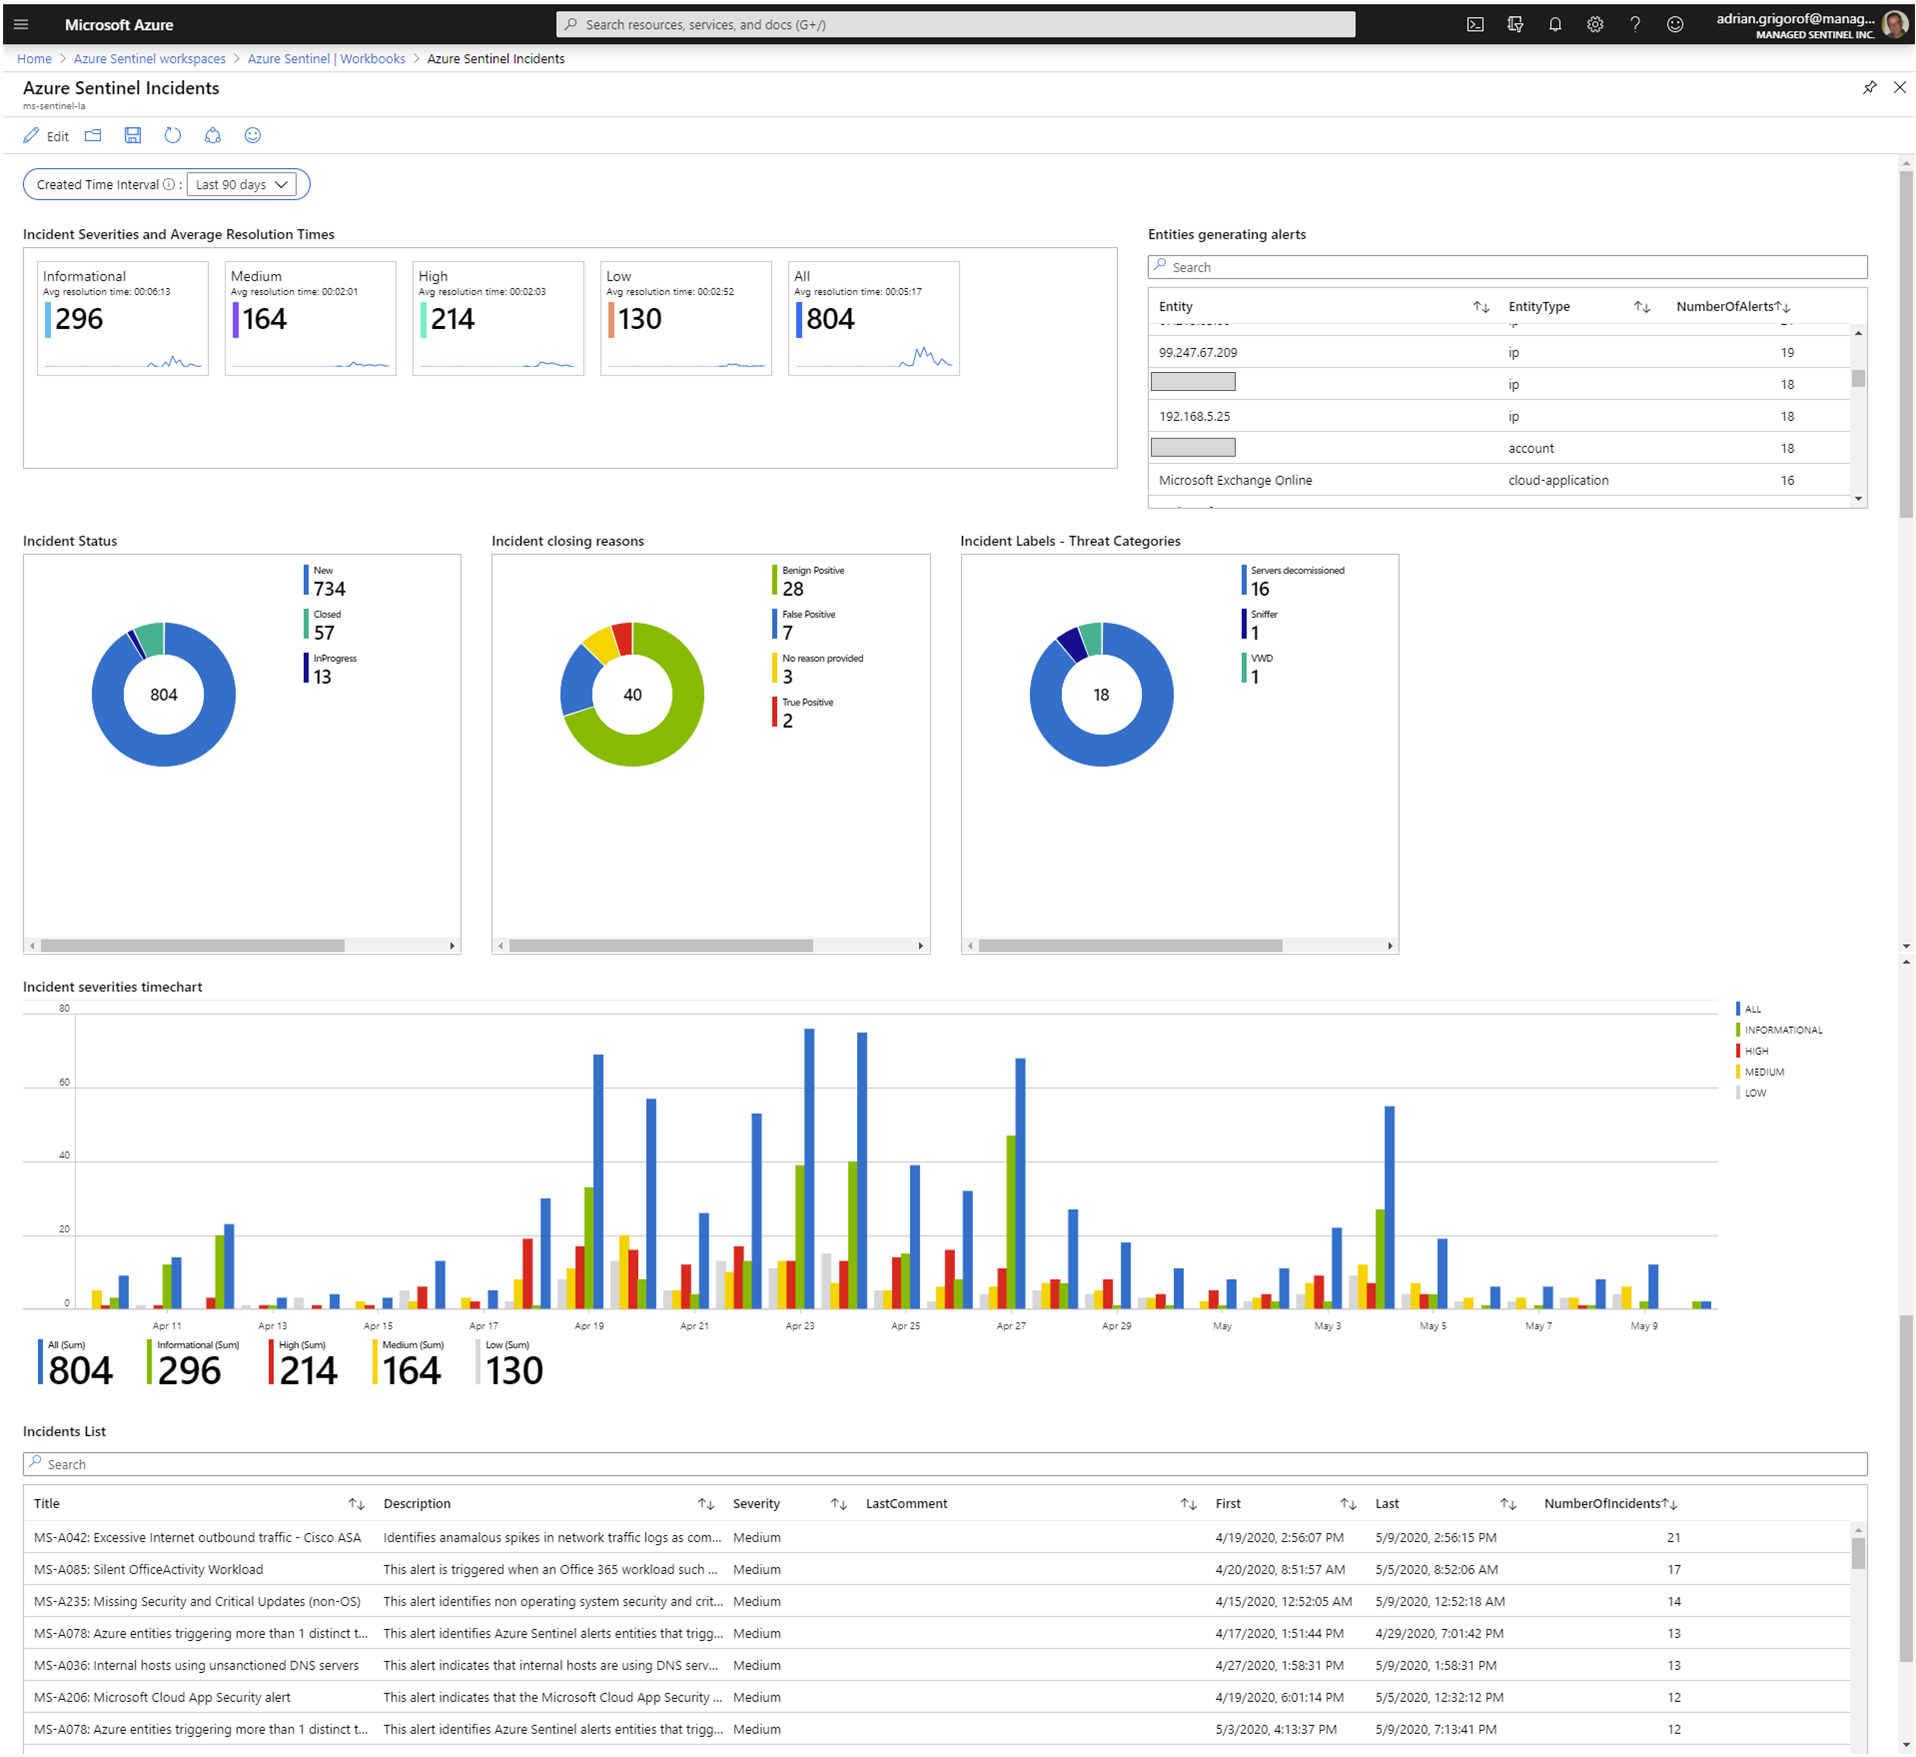
Visualize your data using workbooks in Microsoft Sentinel | Microsoft Learn
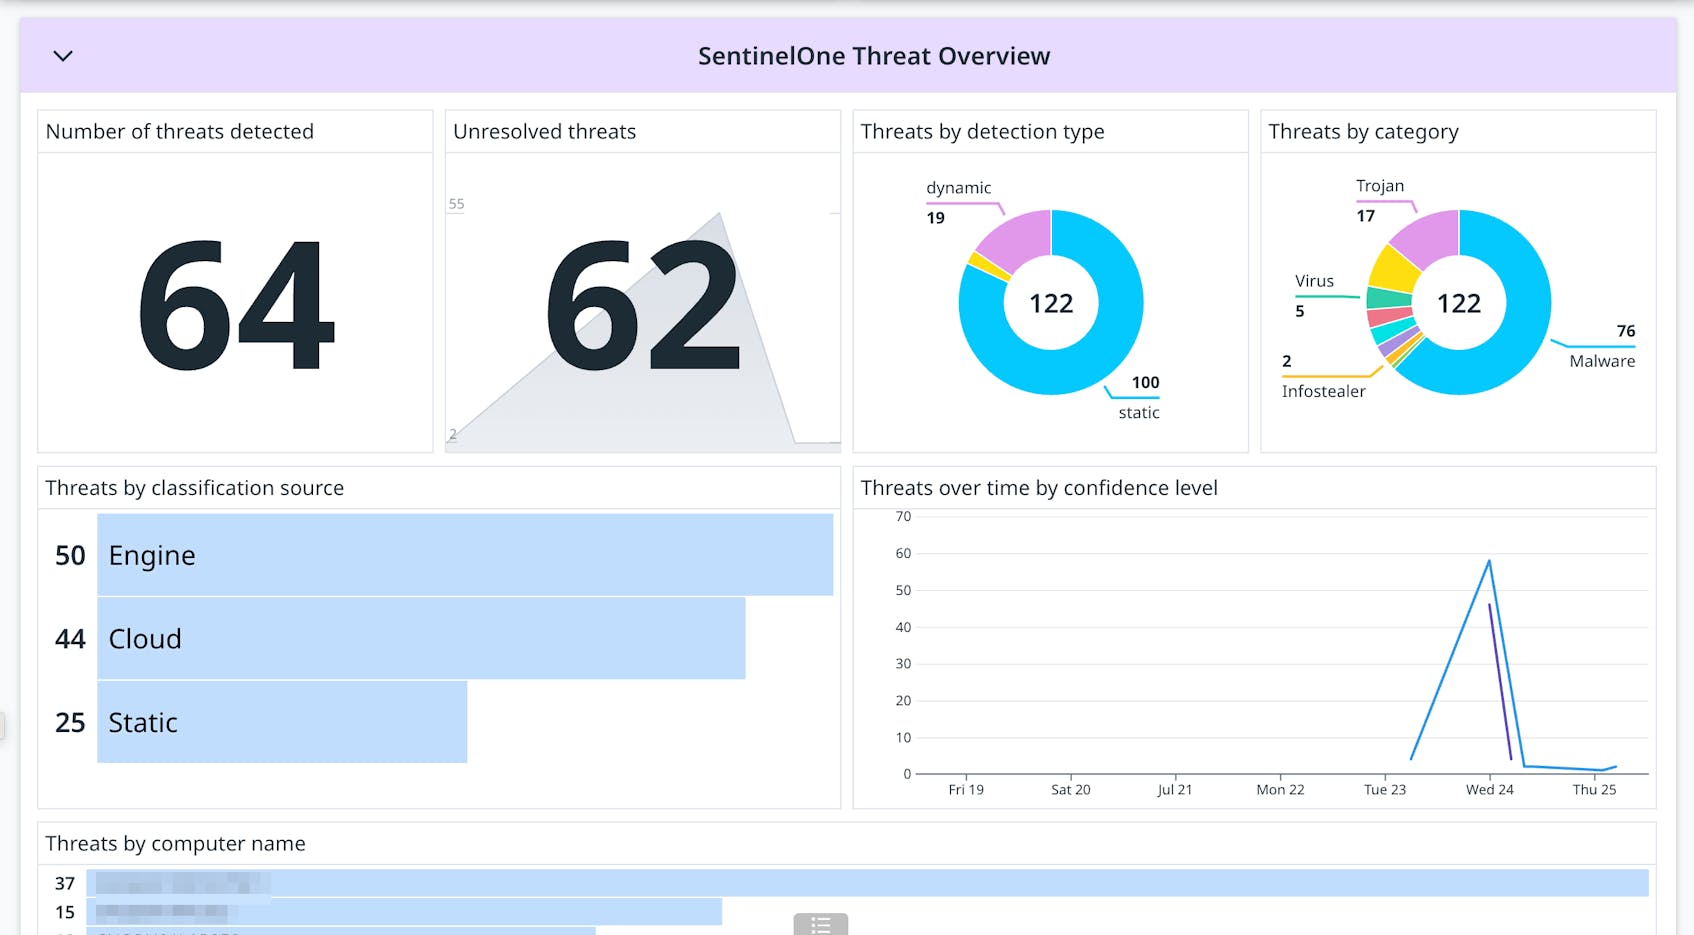
Monitor Your SentinelOne Logs and Alerts With Datadog Cloud SIEM | Datadog
Using Dynamic Data Types in Sentinel | Community
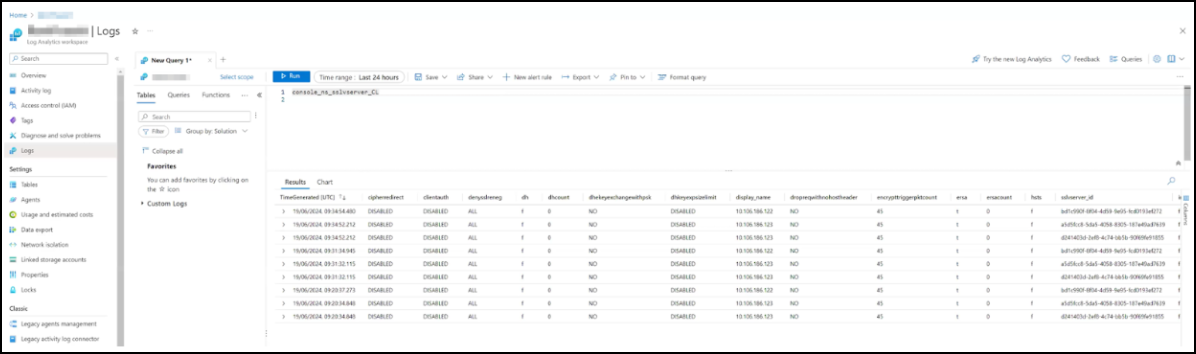
Integration with Microsoft Sentinel | NetScaler Console 14.1
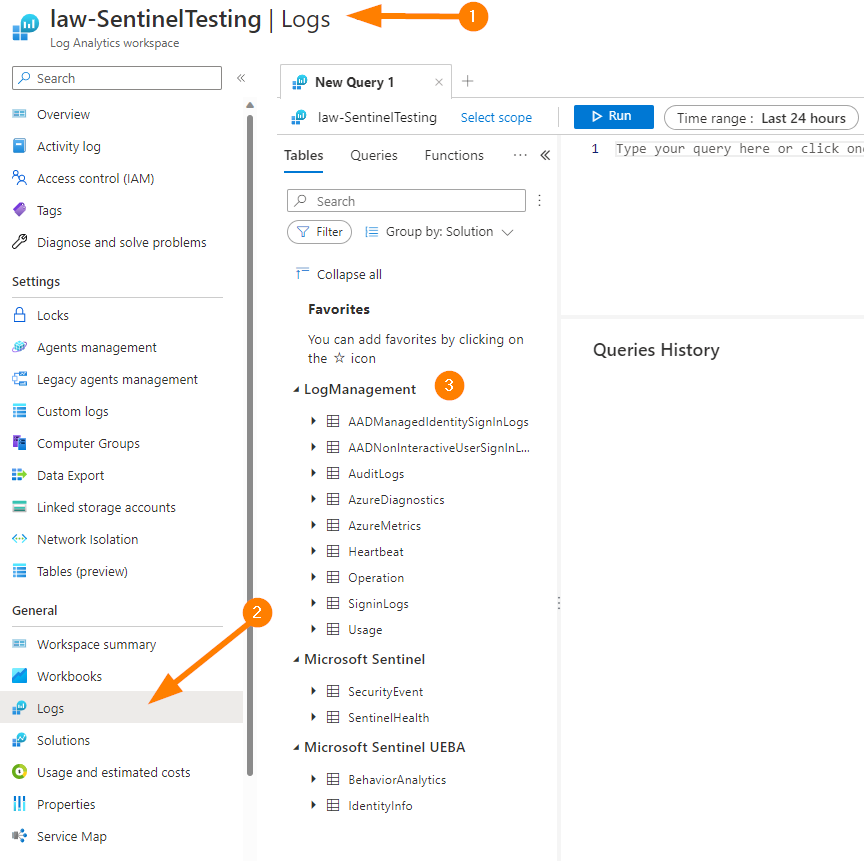
Azure Sentinel Log Analytics step-by-step
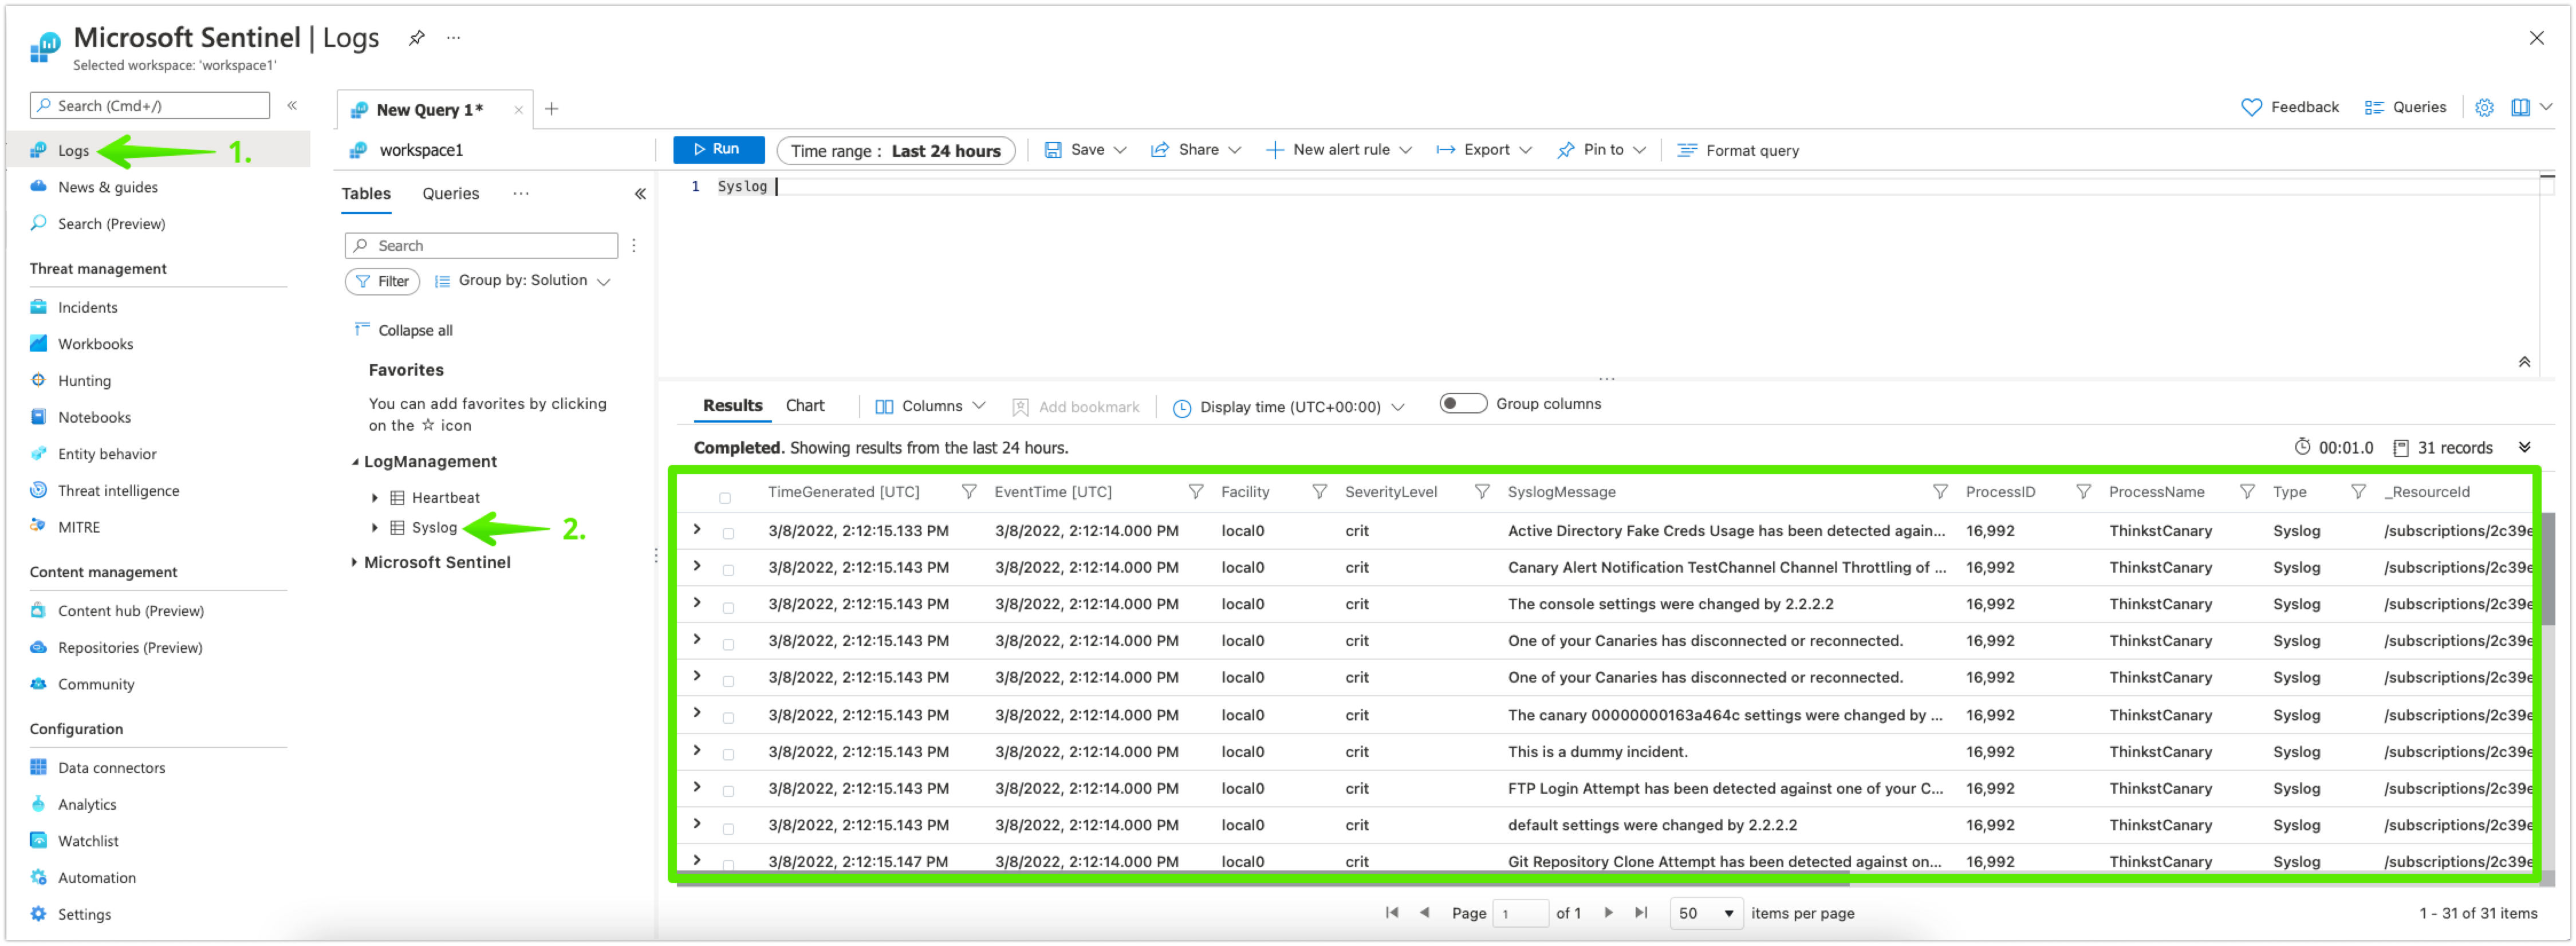
Sending alerts to Microsoft Sentinel with syslog – Thinkst Canary
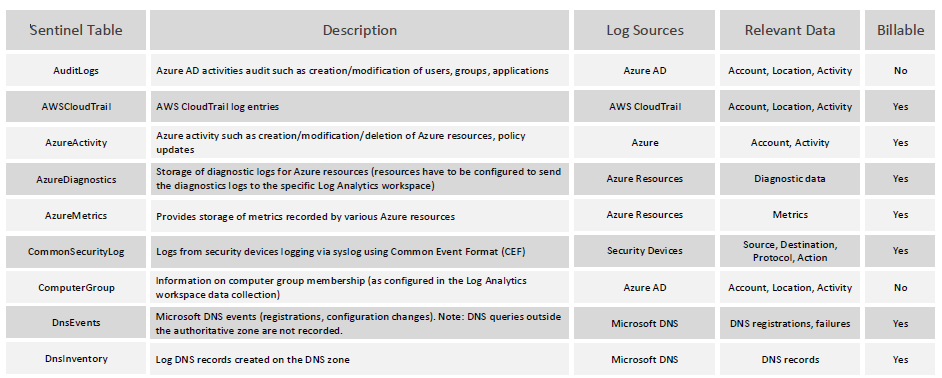
Azure Sentinel & Log Analytics Tables | Managed Sentinel
Sentinel Data Connector Health Monitoring – AzureTracks
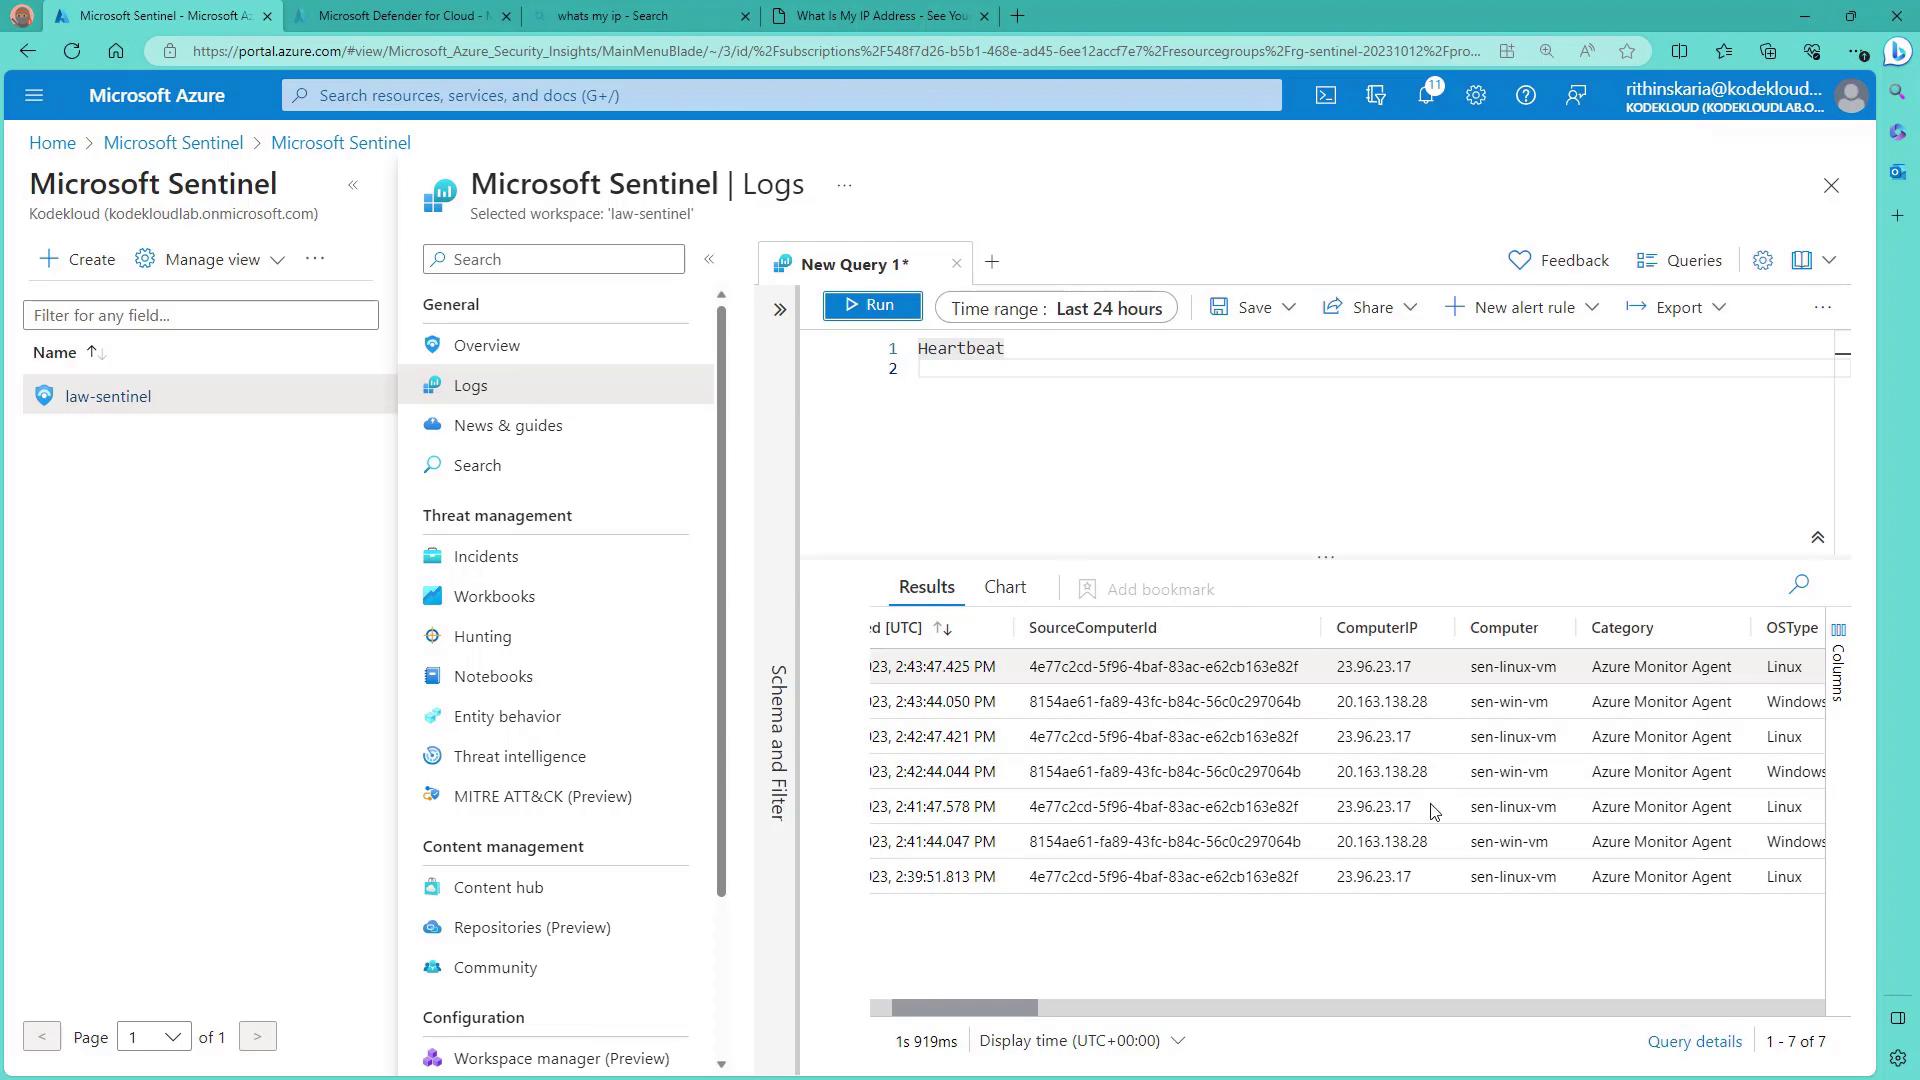
Configure data connections to Sentinel - KodeKloud
Sentinel & Log Analytics – Where is my Data? – AzureTracks
Archiving Azure Sentinel Logs: A Comprehensive Guide to Archive Options ...
Sentinel Log Collector Windows 10 – IRCVP
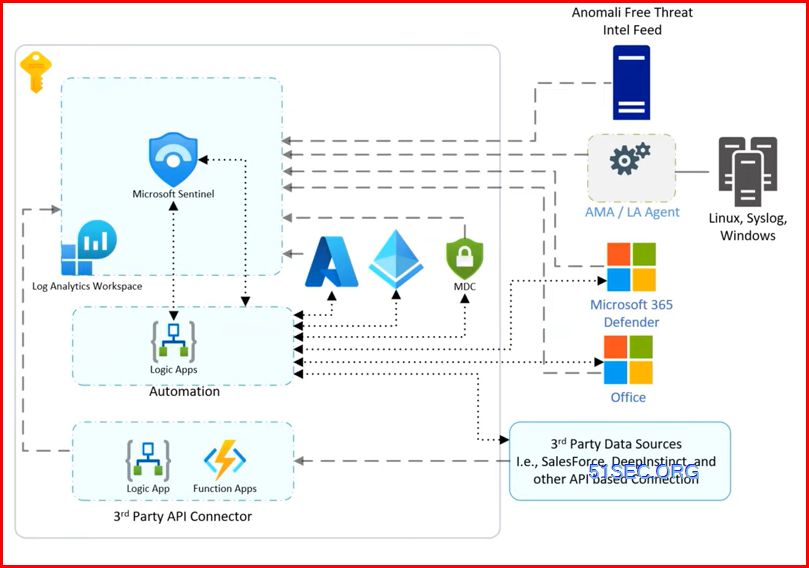
Azure Sentinel Onboarding Different Log Sources - NetSec
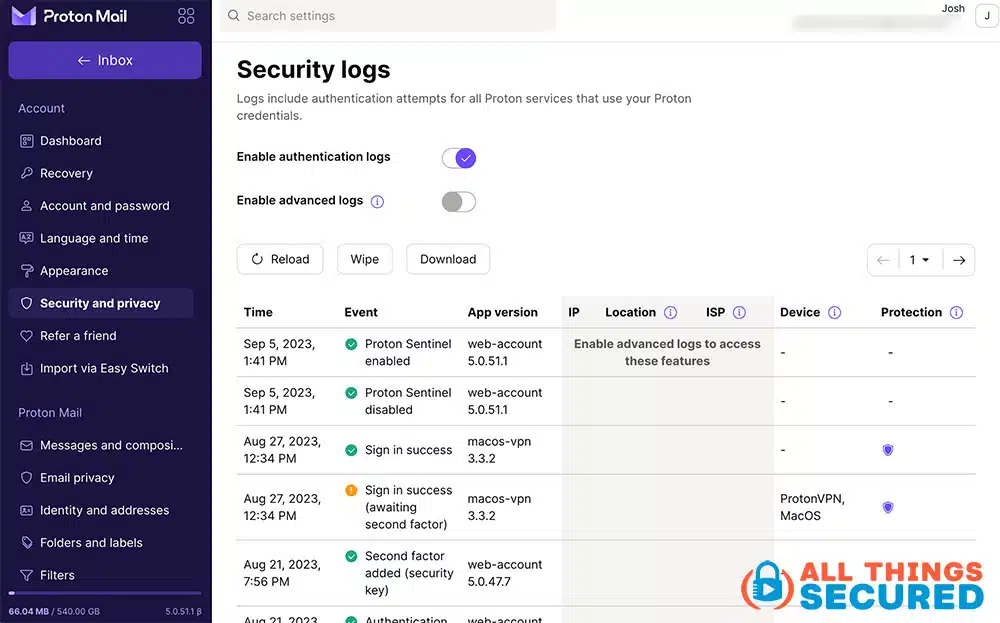
What is Proton Sentinel (and should you use it?)
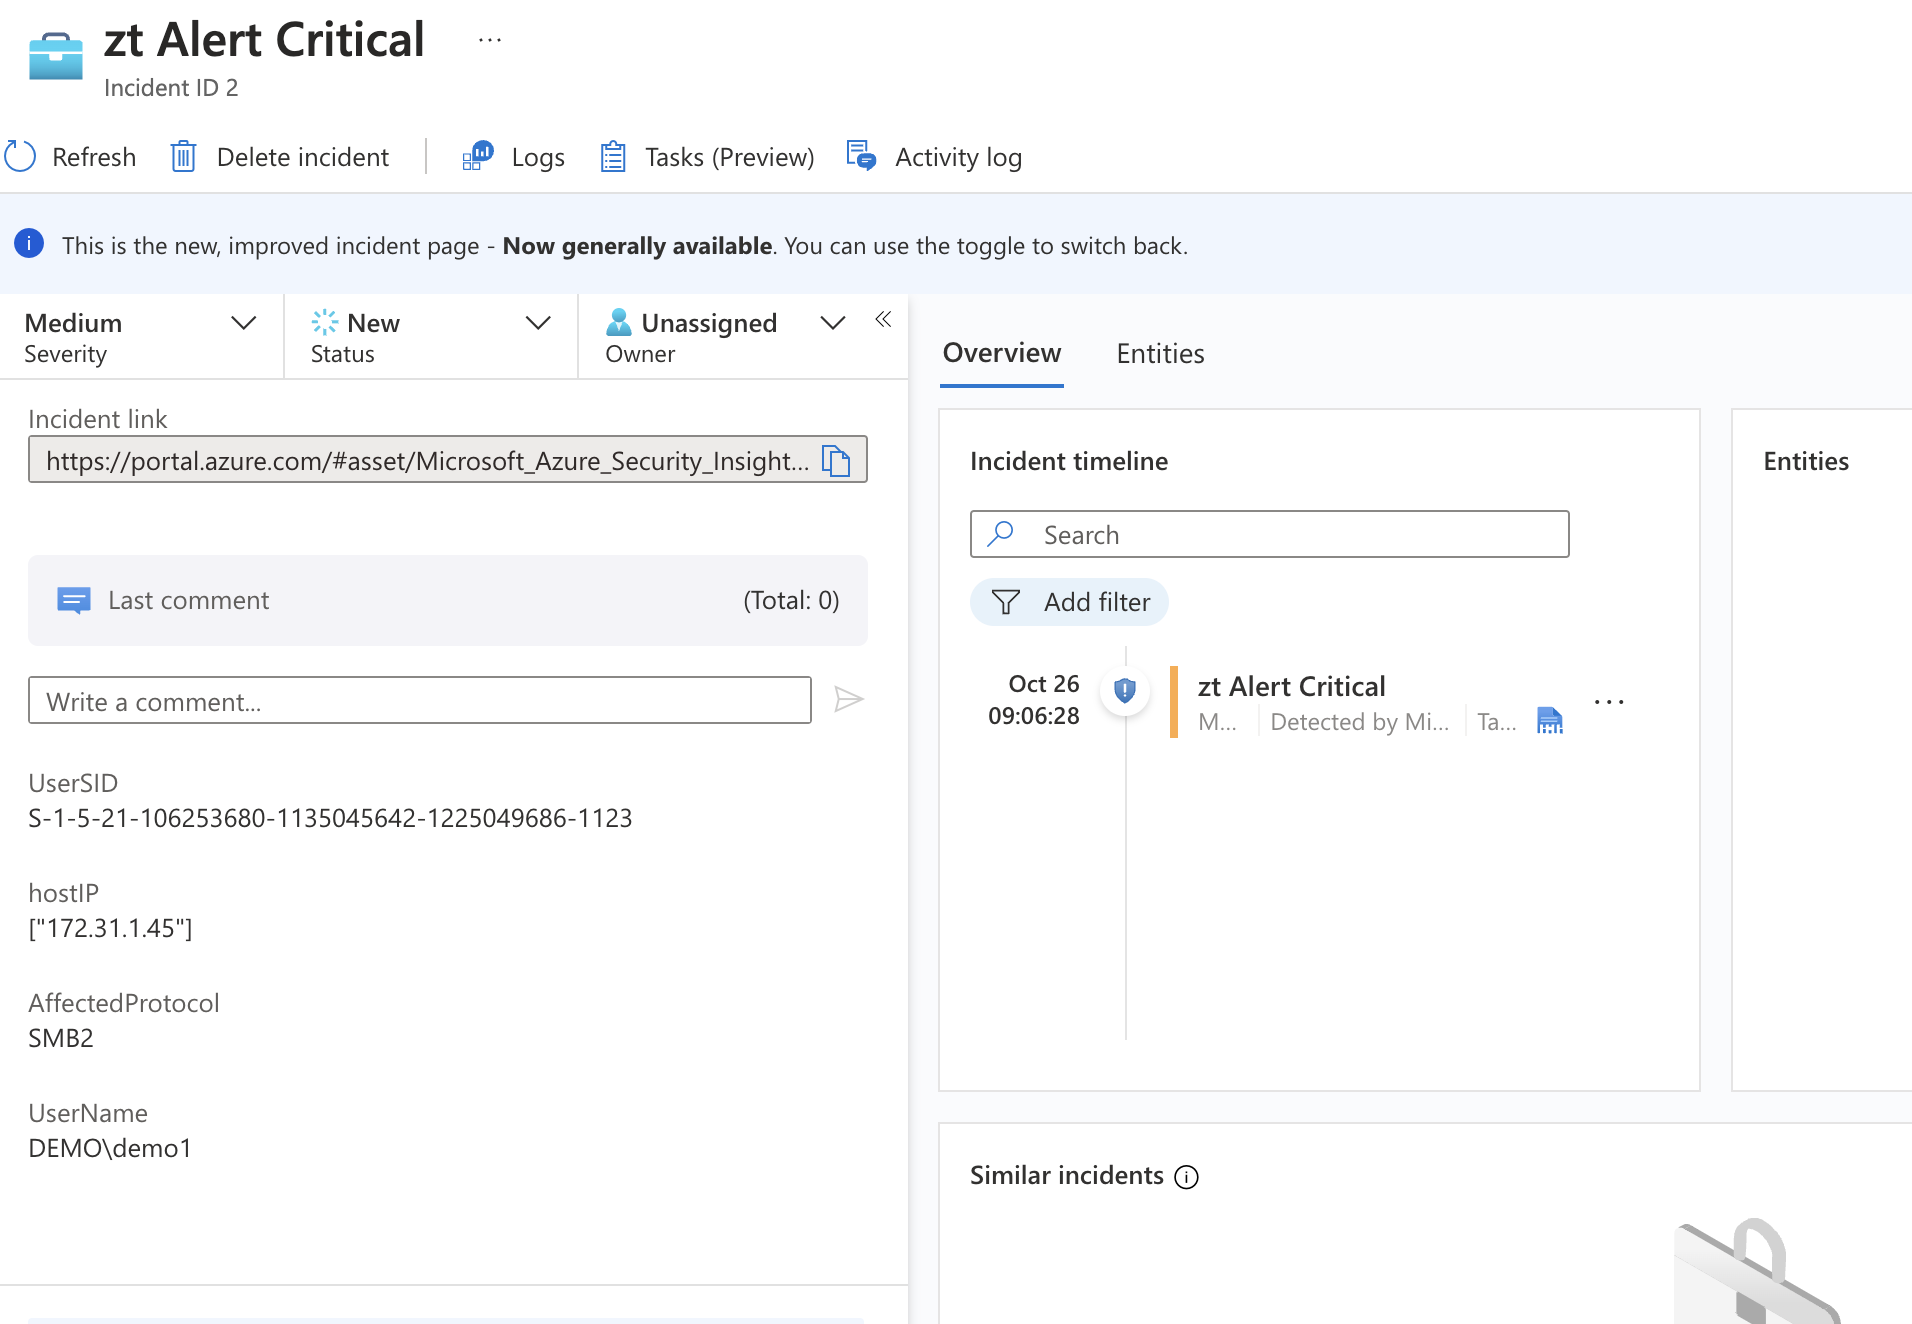
Sentinel Incident integration and Log Analytics Logging with Zero Trust ...
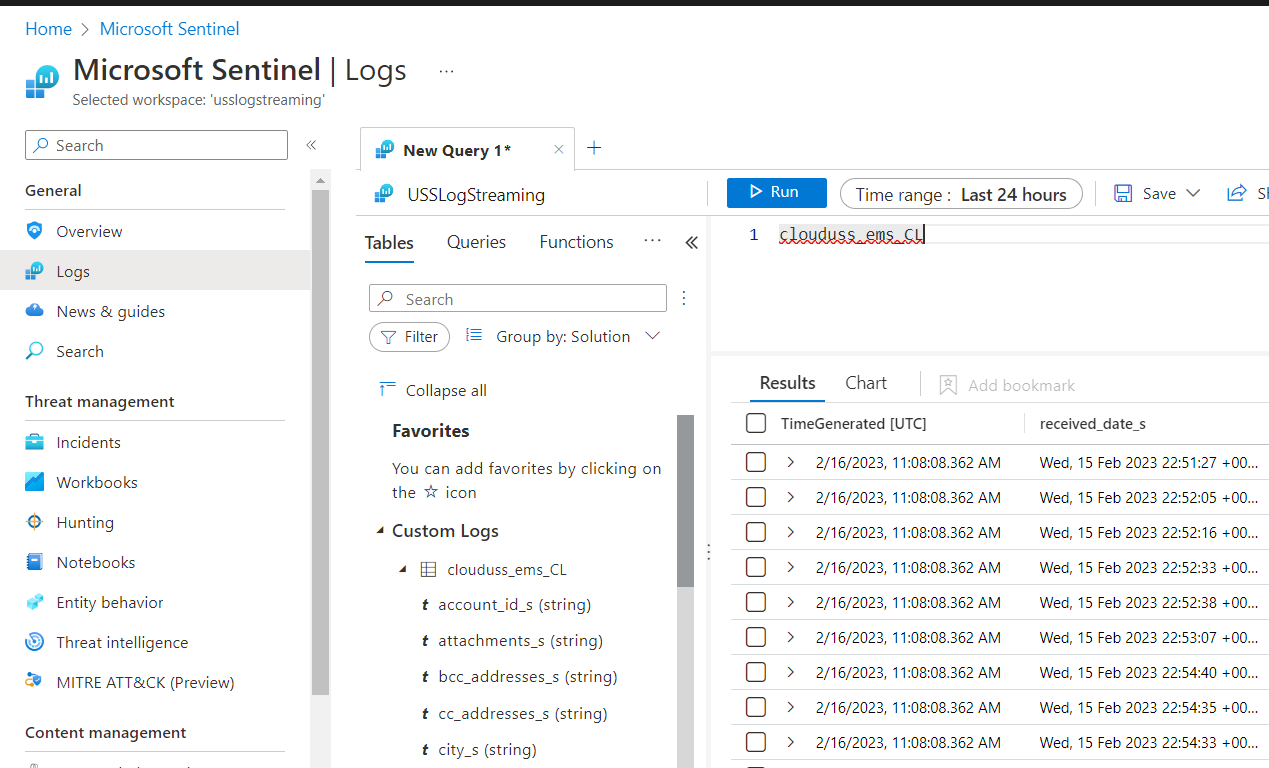
Log Streaming to Microsoft Sentinel - Help :: Unified Security Service
Ingest Custom Logs to Microsoft Sentinel: A Step-by-Step Guide 21
Log retention plans in Microsoft Sentinel | Microsoft Learn
Centrally process and govern your logs in Datadog before sending them ...
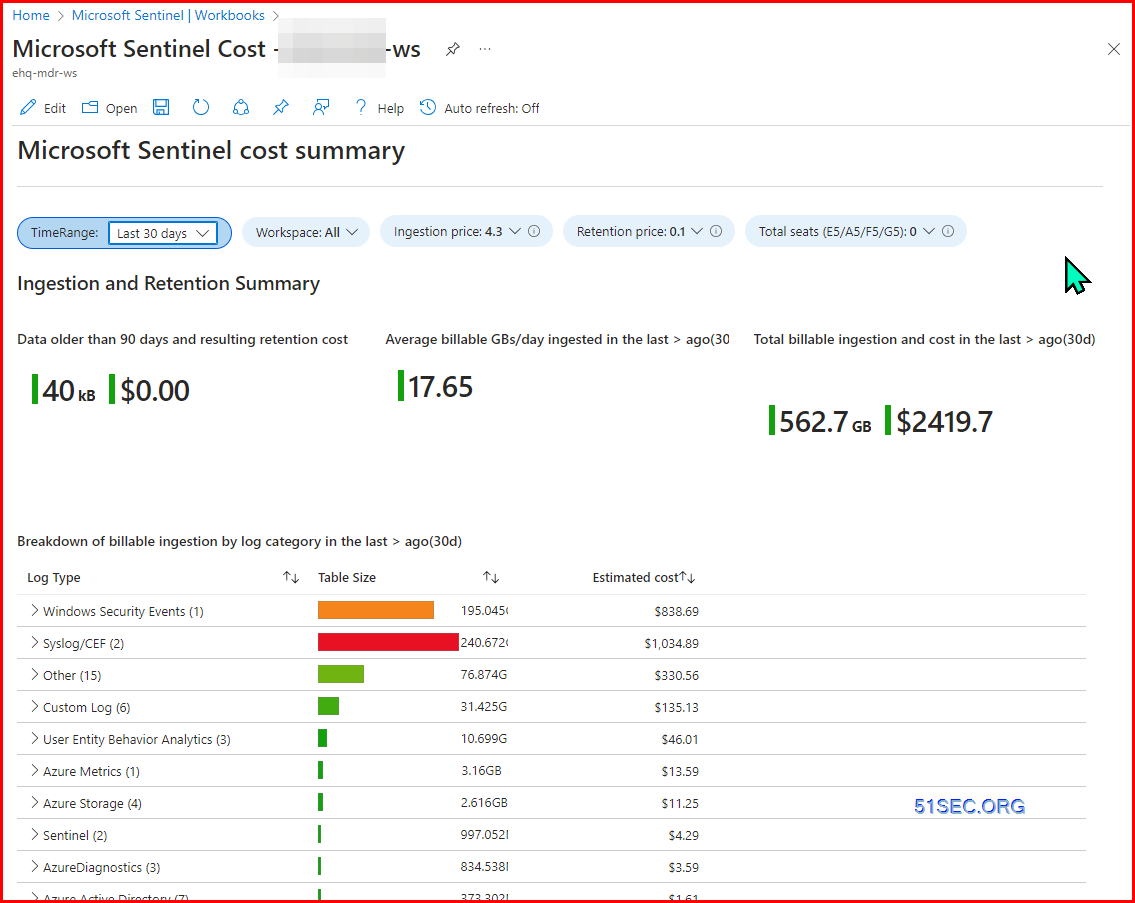
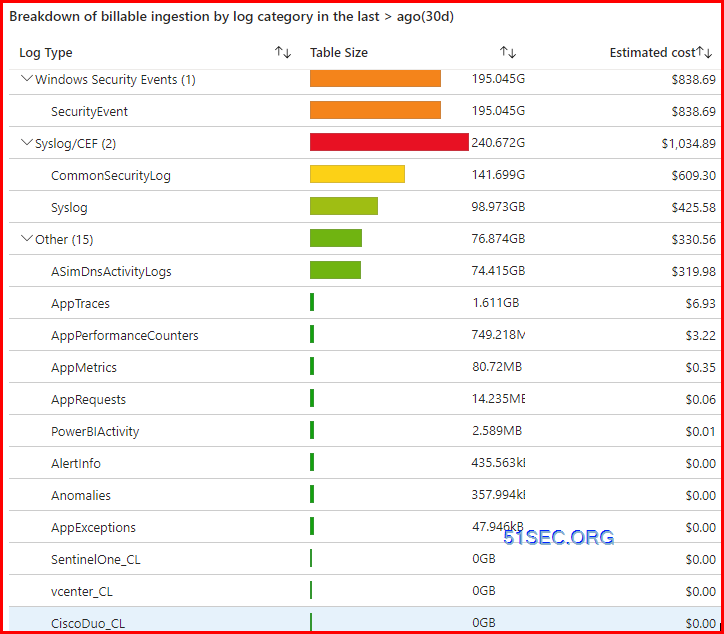
Surpress Azure Sentinel Log Ingestion Volume to Reduce Cost - NetSec
Monitor Log Flow For Devices in Microsoft Sentinel 8
How to collect SentinelOne Agent logs on Linux Machine
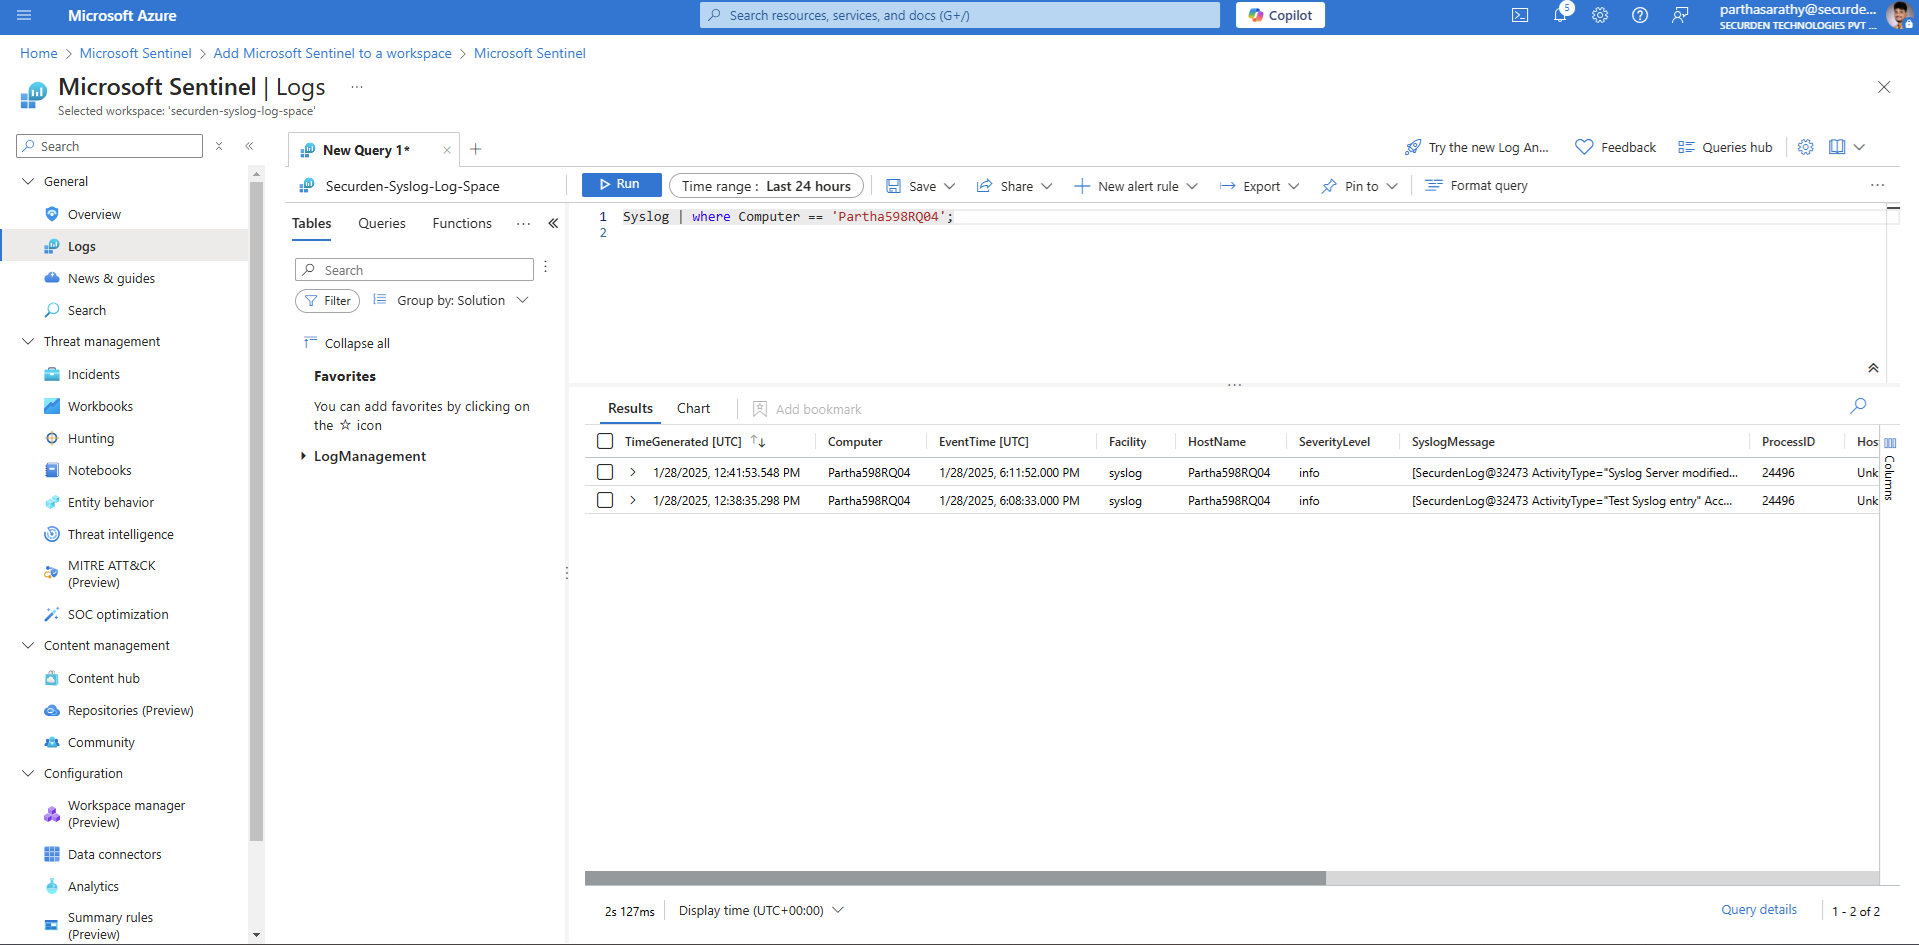
How to Integrate Azure Sentinel for Collecting Syslog | Securden EPM
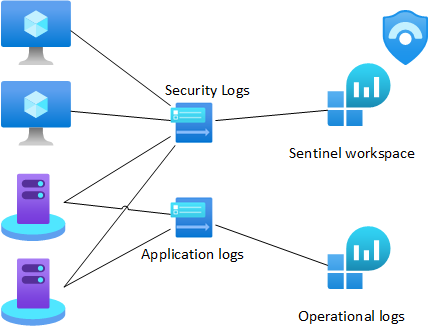
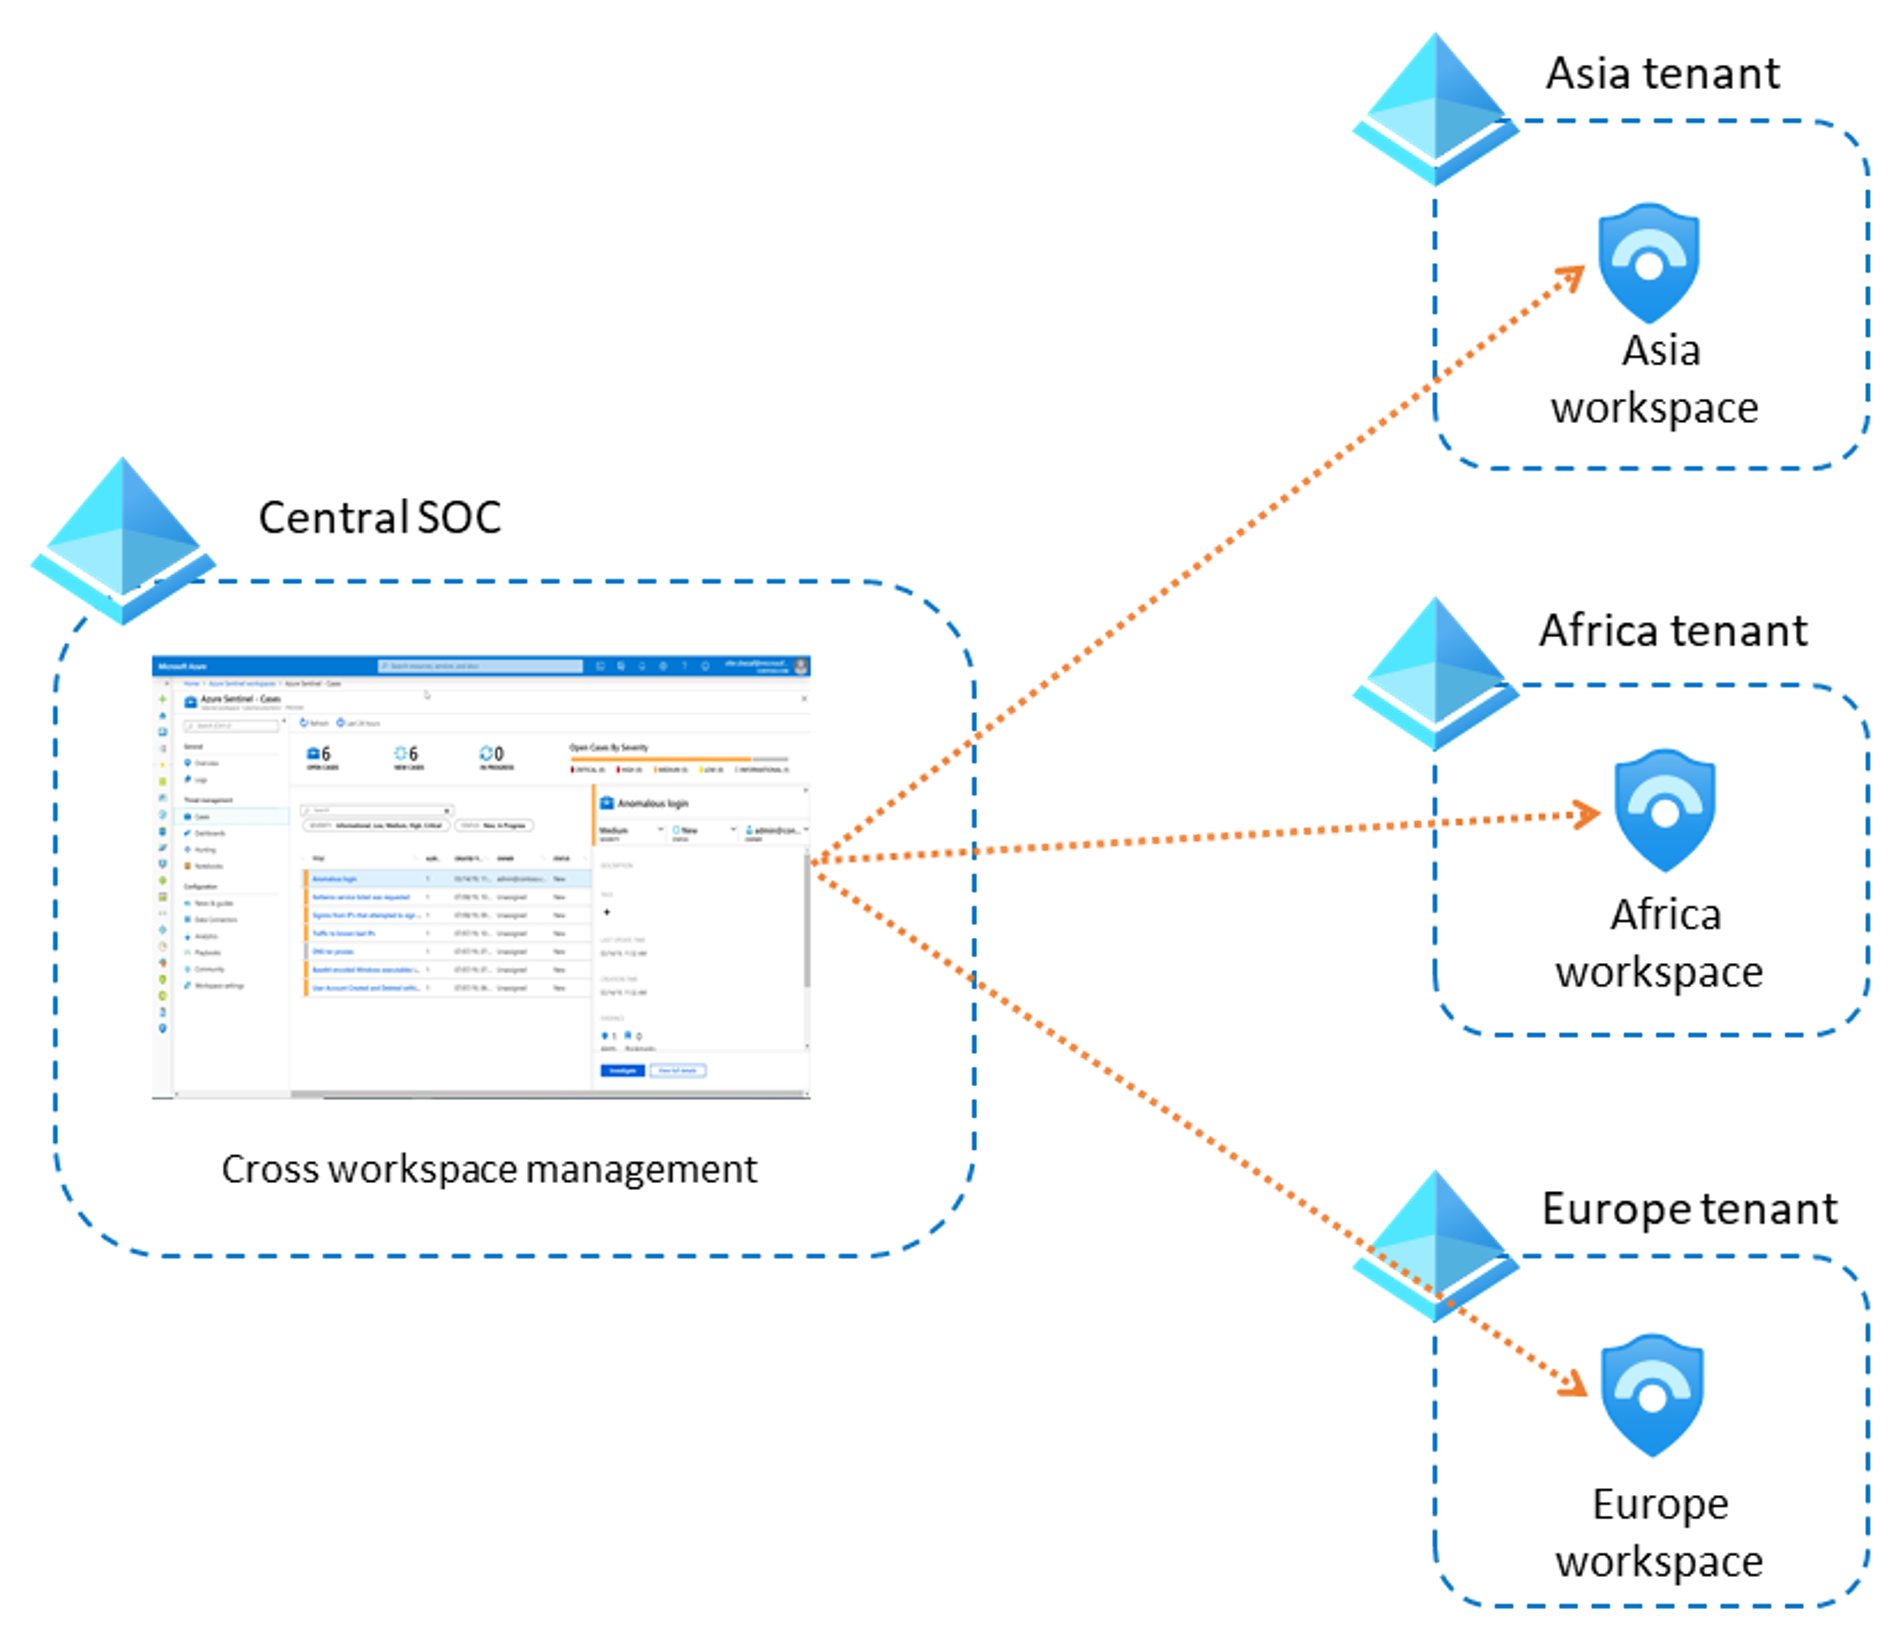
Sample Microsoft Sentinel workspace designs | Microsoft Learn
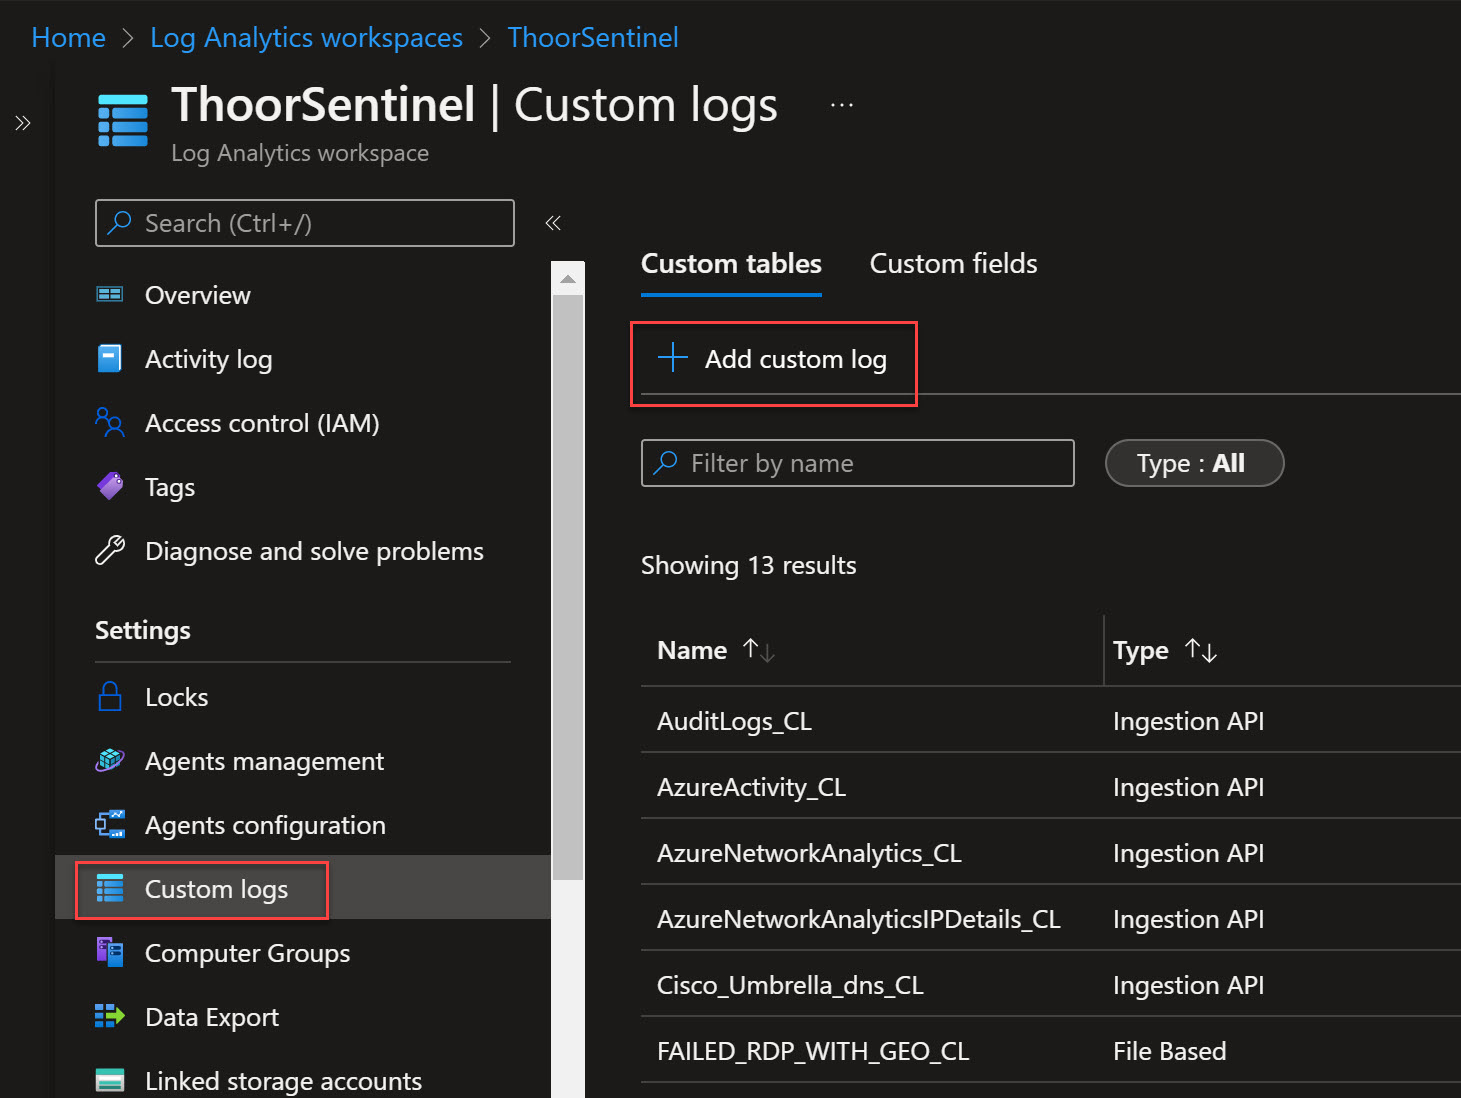
RDP Honeypot and Microsoft Sentinel Workbook - thoor.tech
Azure Sentinel Log Sources – Best practices for Microsoft Sentinel – EHNCA
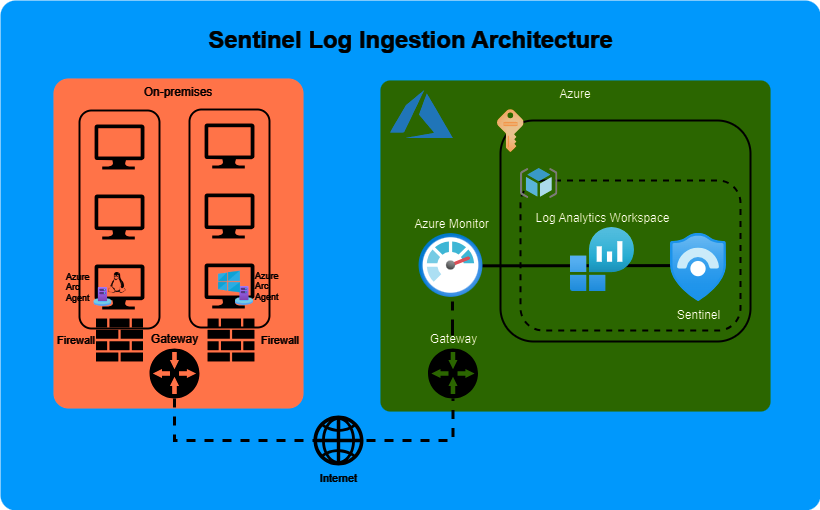
How To Ingest Logs From On-Premises Windows Server To Microsoft ...
Azure のための Microsoft Sentinel: Sentinel 必要か – ALJK
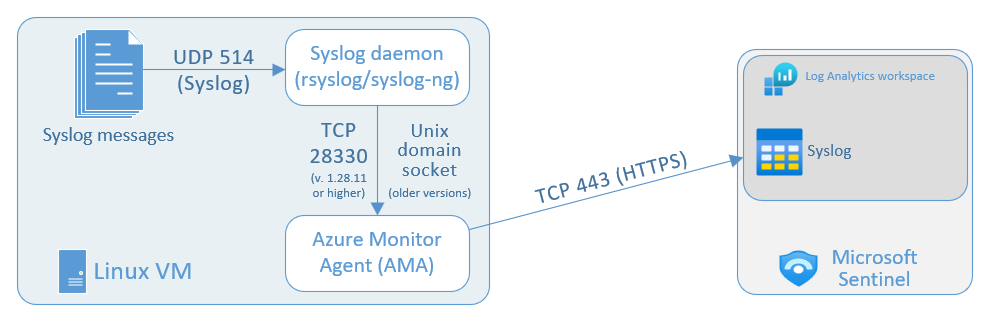
Set Up Syslog Forwarding to Microsoft Sentinel
Ingest Custom Logs to Microsoft Sentinel: A Step-by-Step Guide 24
How to use Microsoft Sentinel with Office 365 to find risks | TechTarget
Microsoft Sentinel migration: Update SOC and analyst processes | Azure Docs
Responding to Incidents in Microsoft Sentinel – AzureTracks
Top 7 Azure Reporting Tools for Efficient Data Management
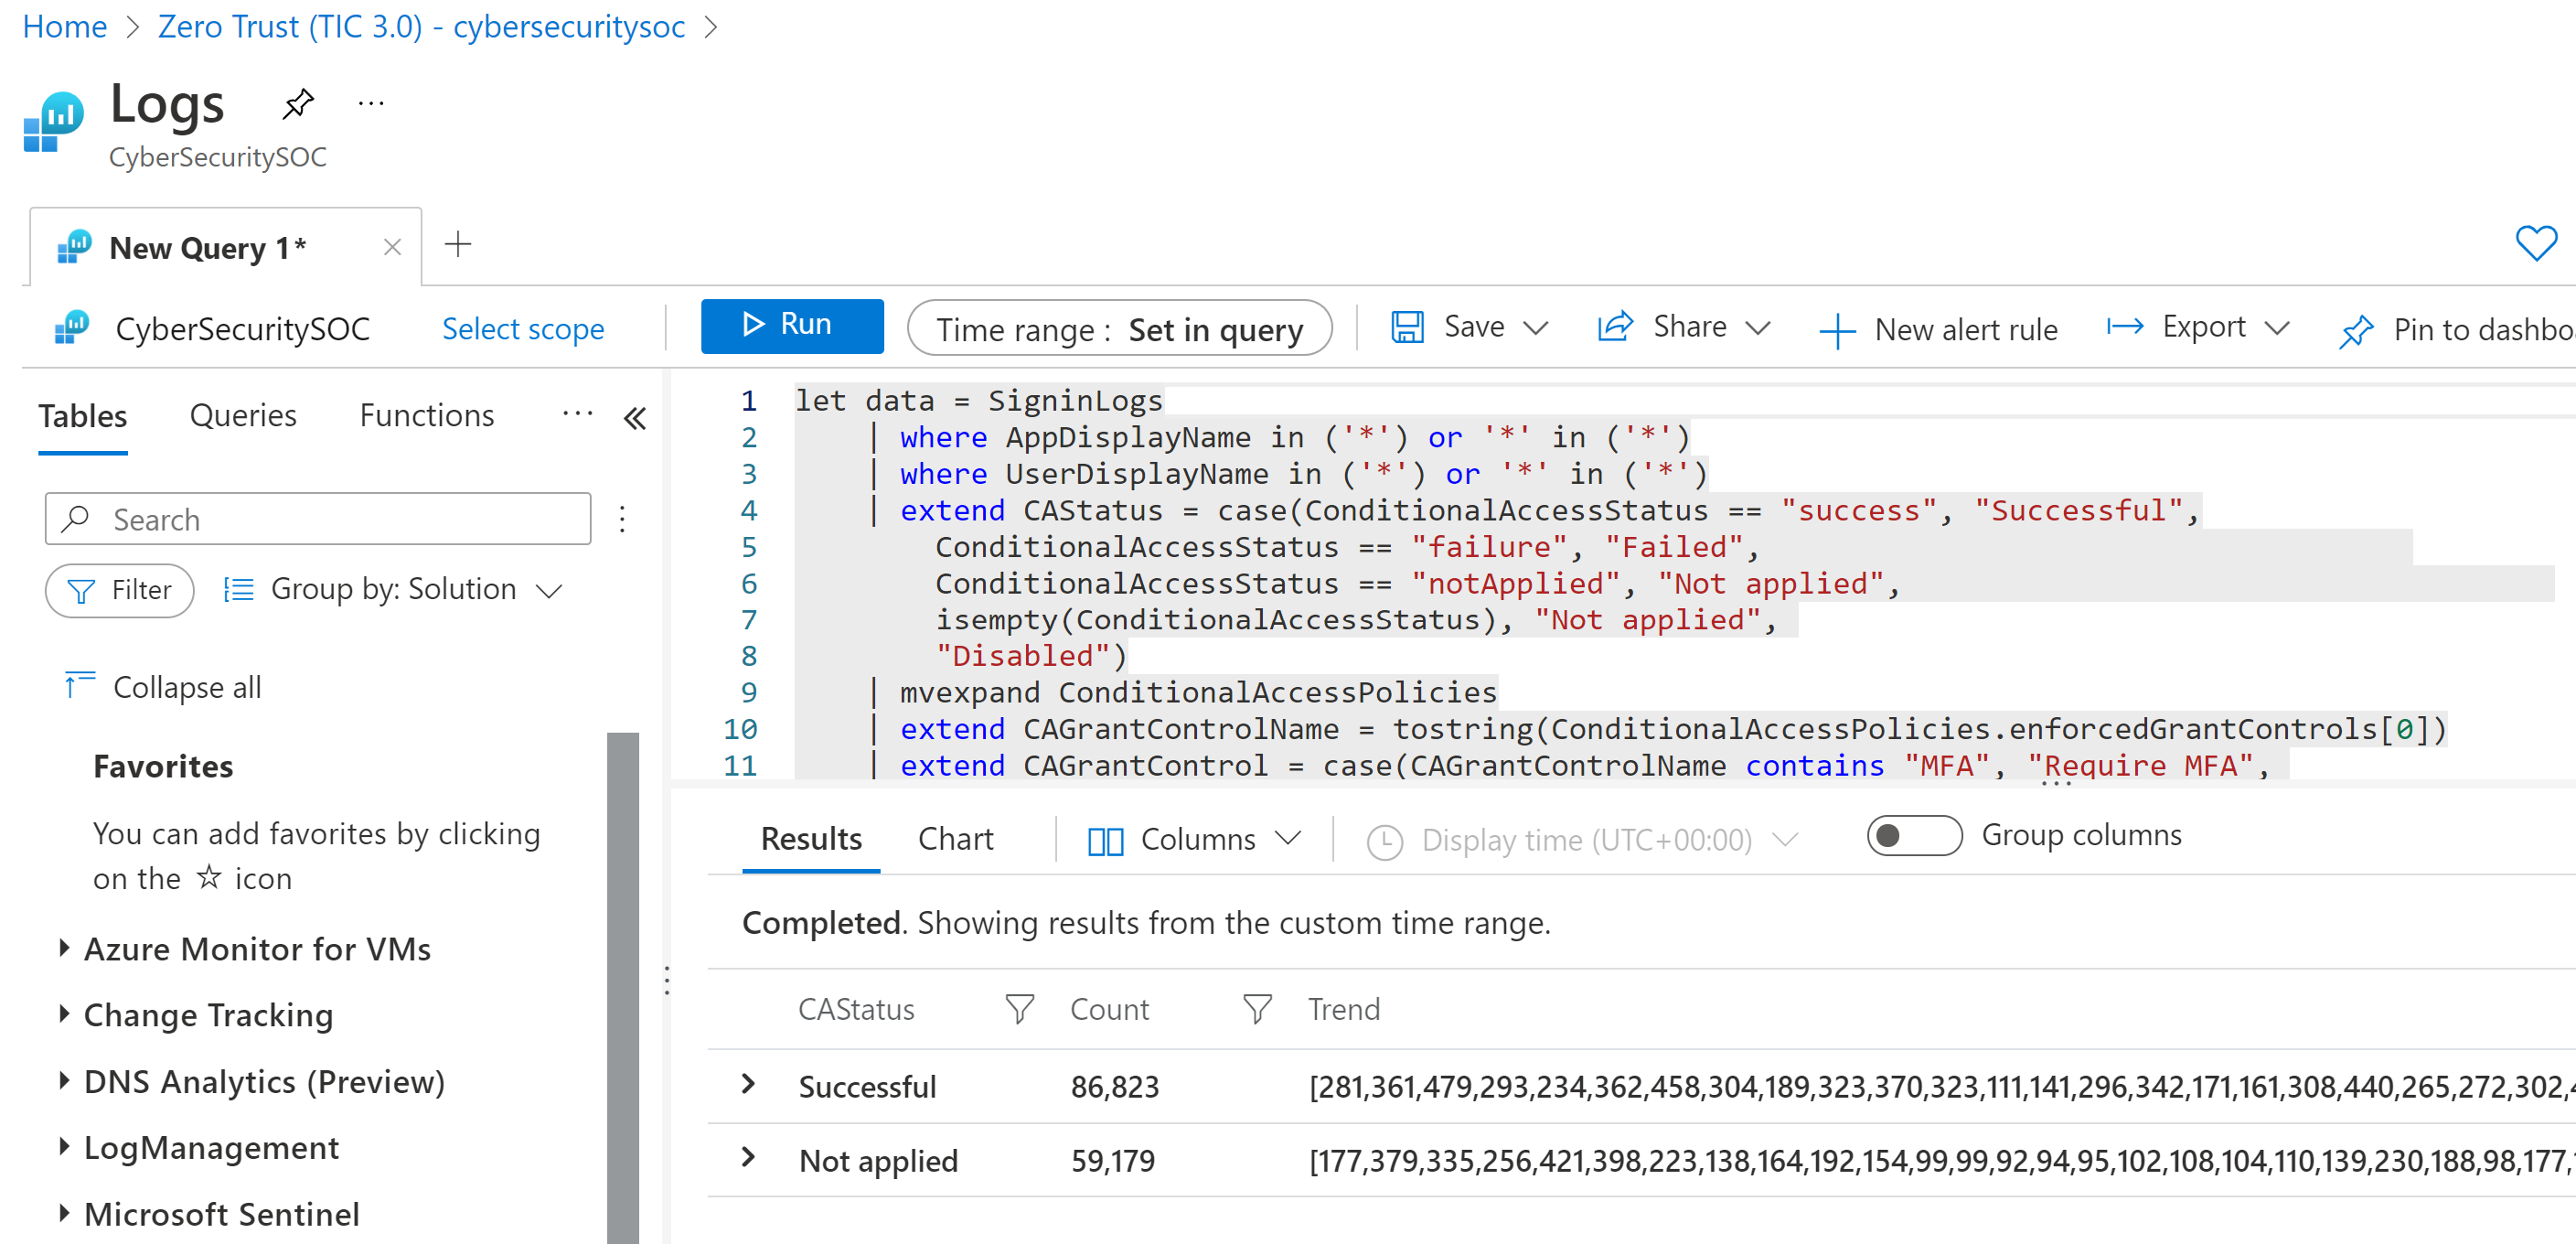
Monitor Zero Trust (TIC 3.0) security architectures with Microsoft ...
Collect, detect, investigate, and respond to security threats using ...
Microsoft Sentinel's Audit Logs: Monitor Activity, Respond to Threats ...
CTF Writeup: MS Sentinel: Just Looking | CTFs | OSINT | InfoSec
Sentinel-Log-Ingestion-Resiliency | EXMDR
Sentinel/Adverse Events Logbook | PDF
Azure HomeLabs | Isaac Park blog
dbi Blog
Configuring Data Connector And Producing Activity Data in Microsoft ...
Getting Started with Microsoft Azure Sentinel: Part 2
SentinelOne
TryHackMe | SOC Alert Triaging - Tinsel Triage
Sentinel: Log Analytics - by Tristan K